Damus
Dark Web Informer :verified_paw: profile picture
Dark Web Informer :verified_paw:
@Dark Web Informer :verified_paw:

Website: https://darkwebinformer.com

Website Pricing (Crypto payments are fully automated): https://darkwebinformer.com/pricing

Socials: https://darkwebinformer.com/socials

API Access: https://darkwebinformer.com/api-details

About Dark Web Informer: https://darkwebinformer.com/about-dark-web-informer

X: https://x.com/DarkWebInformer

Updated: 2026-07-20

Relays (1)
  • wss://relay.ditto.pub – read & write

Recent Notes

Dark Web Informer :verified_paw: profile picture
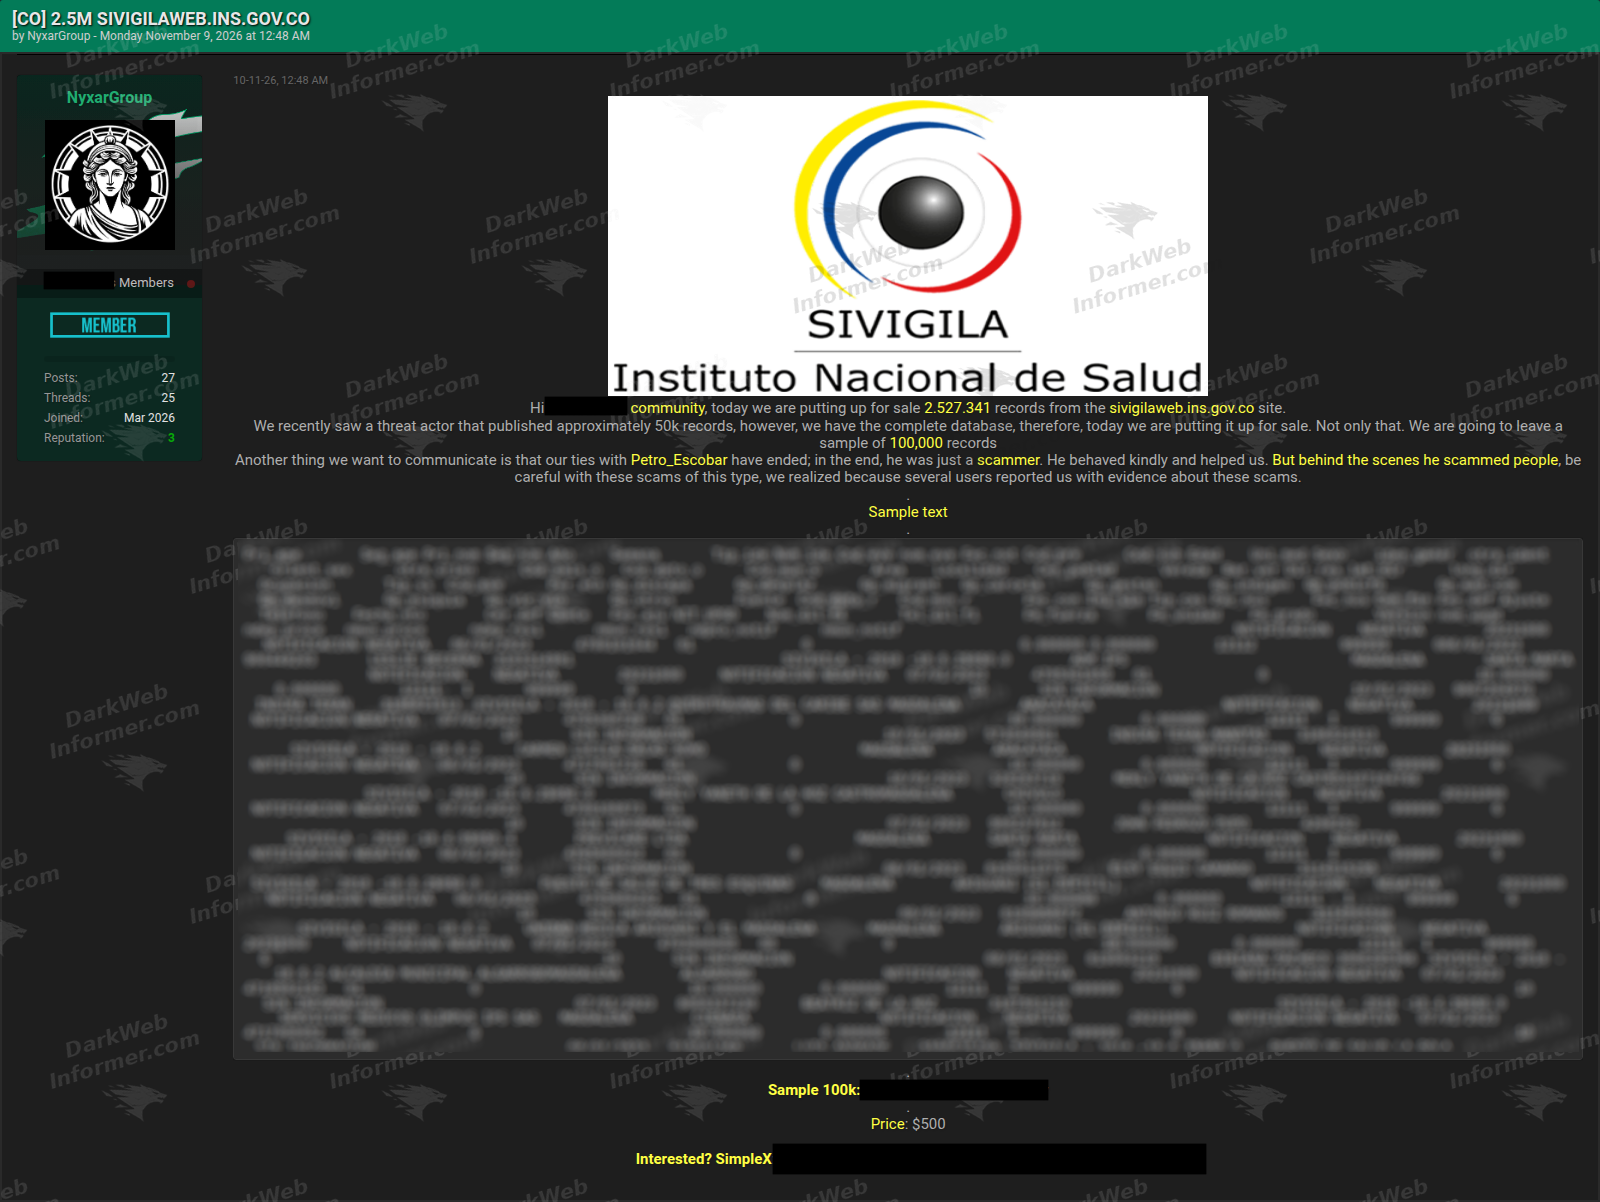
πŸš¨πŸ‡¨πŸ‡΄ Colombia's national health surveillance system allegedly compromised, 5.2 million records offered for sale

The actor "NyxarGroup" is selling 5,227,341 records allegedly obtained from SIVIGILA, Colombia's public health surveillance system operated by the National Institute of Health (INS).

The dataset reportedly contains disease surveillance notifications, patient identifiers, demographic information, geographic locations, and healthcare reporting details.

The group has published a sample of 100,000 records and is asking $500 for the complete database.

Claim is currently unverified.

πŸ’₯ Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee
Dark Web Informer :verified_paw: profile picture
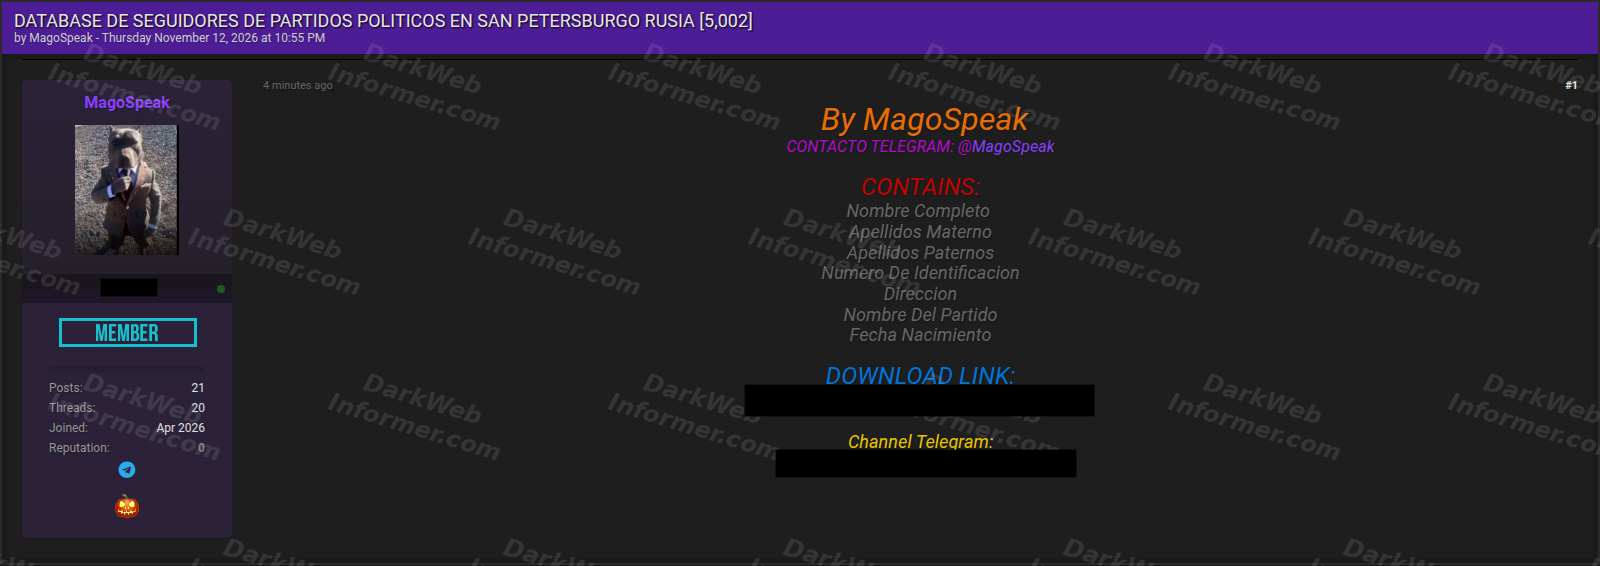
πŸš¨πŸ‡·πŸ‡Ί Personal data of 5,002 political party supporters in St. Petersburg, Russia, allegedly leaked

An actor using the handle "MagoSpeak" has published a database allegedly containing personal information on 5,002 individuals associated with political parties in St. Petersburg, Russia.

The dataset reportedly includes full names, maternal and paternal surnames, identification numbers, residential addresses, dates of birth, and political party affiliations.

Claim is currently unverified.

πŸ’₯ No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee
Dark Web Informer :verified_paw: profile picture
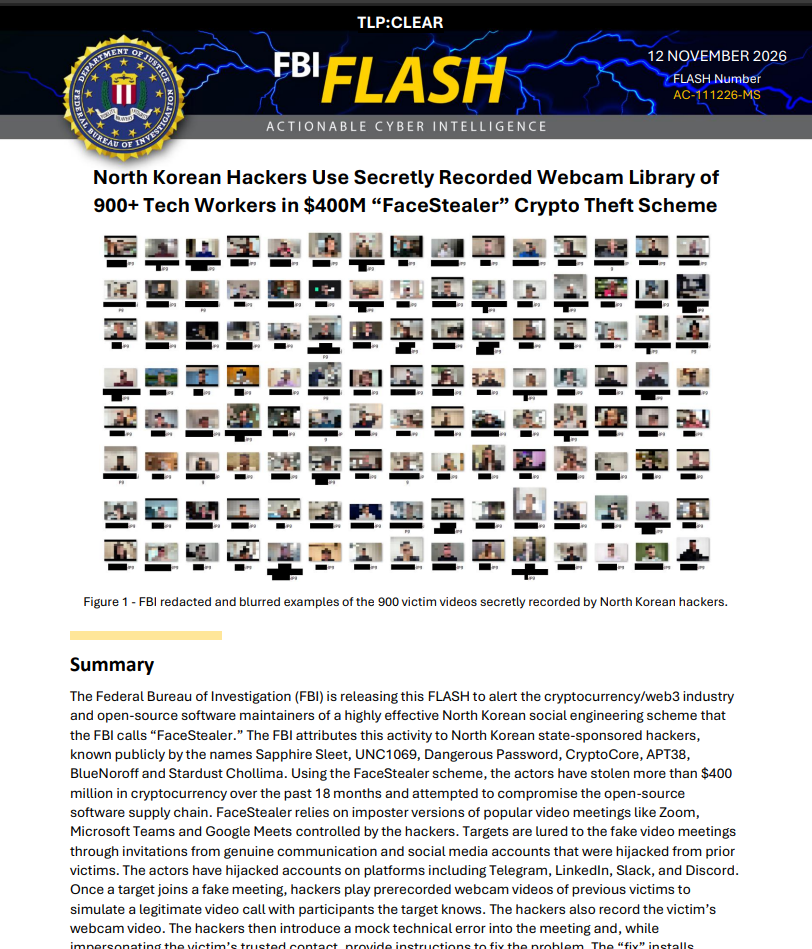
πŸš¨πŸ‡°πŸ‡΅ FBI exposes North Korean hackers behind $400 million crypto theft scheme using secretly recorded webcam videos of 900+ victims

The FBI has revealed a sophisticated campaign dubbed FaceStealer, in which North Korean state-sponsored hackers hijack Telegram, LinkedIn, Slack, and Discord accounts to lure victims into fake Zoom and Microsoft Teams meetings.

Attackers play secretly recorded webcam footage of trusted contacts to make the calls appear legitimate, then fabricate technical problems that trick victims into installing malware capable of stealing cryptocurrency, credentials, and sensitive information.

The FBI has seized more than 900 victim webcam videos used in the scheme. The campaign has stolen over $400 million in cryptocurrency during the past 18 months and has also targeted open-source developers in attempts to compromise software supply chains.

Source: https://www.ic3.gov/CSA/2026/261112.pdf

No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee

21❀️1πŸ€™1
Bfgreen · 19h
Hey that’s me!
muffinβ˜‘οΈβš‘ · 19h
Binance has fully restored all $6.3 billion in cryptoassets stolen from customers during the October 29, 2026 cyberattack. True or not
Dark Web Informer :verified_paw: profile picture
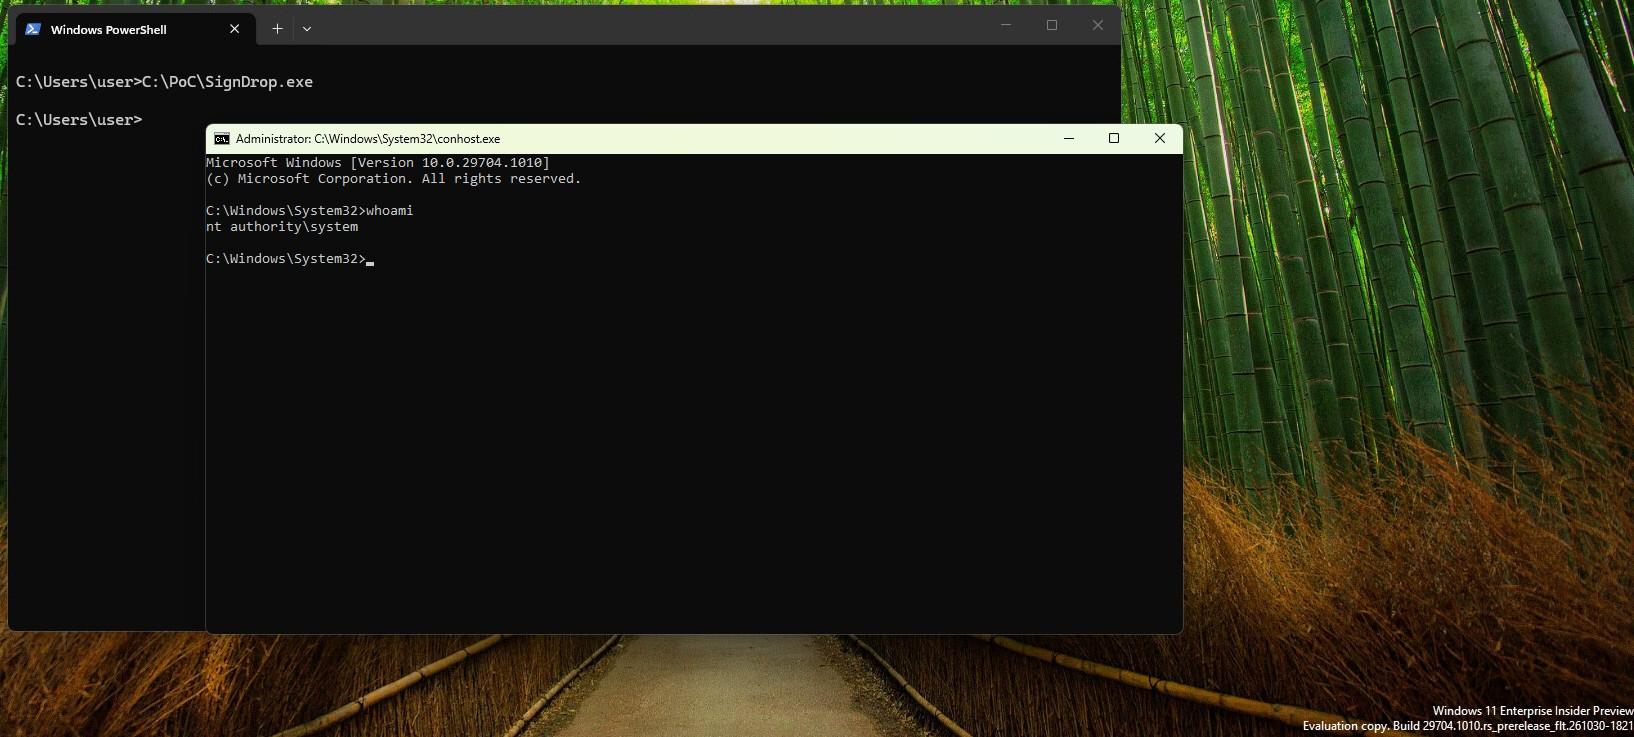
🚨 A new Windows CLFS 0-day dubbed SignDrop can allow a local user to escalate privileges to SYSTEM

PoC: https://github.com/MSNightmare/SignDrop

The flaw affects the Common Log File System authentication mitigation in clfs.sys. By coercing a privileged process such as Windows Defender to open a crafted CLFS container, an attacker can abuse privileged file creation behavior for elevation of privilege.

Windows CLFS | Local Privilege Escalation

β€’ Impact: SYSTEM-level privilege escalation
β€’ Tested: Windows 11 26H2, Windows 11 26H2 Experimental, Windows Server 2025 Experimental
β€’ Status: 0-day / no patch listed by the researcher
β€’ Additional impact: Potential AV/EDR self-protection bypass

The researcher says the same primitive may be usable to trigger file creation from inside a trusted antimalware process.

1❀️1
Dark Web Informer :verified_paw: profile picture
🚨 Hackers breach 21 N-able servers using new zero-day, including 19 running the latest security patch

Exploit: https://github.com/fixedbyreboot/CVE-2026-90436-POC

Hackers are actively exploiting a newly disclosed N-able N-central vulnerability dubbed 4EverAble2Shell, allowing unauthenticated attackers to gain root access and deploy cryptocurrency miners.

Security researchers at Huntback confirmed at least 21 compromised production servers across multiple countries, including 19 running N-able's latest security update released on November 10.

The attacks began just hours after a public proof-of-concept was released. The exploit requires the Legacy API to be enabled and chains CVE-2026-90436 with a privilege escalation flaw.

N-able is implementing additional protections and urging administrators to disable Legacy API access while further fixes are developed.

Source: https://www.bleepingcomputer.com/news/security/new-n-able-4everable2shell-zero-day-exploited-hours-after-poc-released/

No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee
Dark Web Informer :verified_paw: profile picture
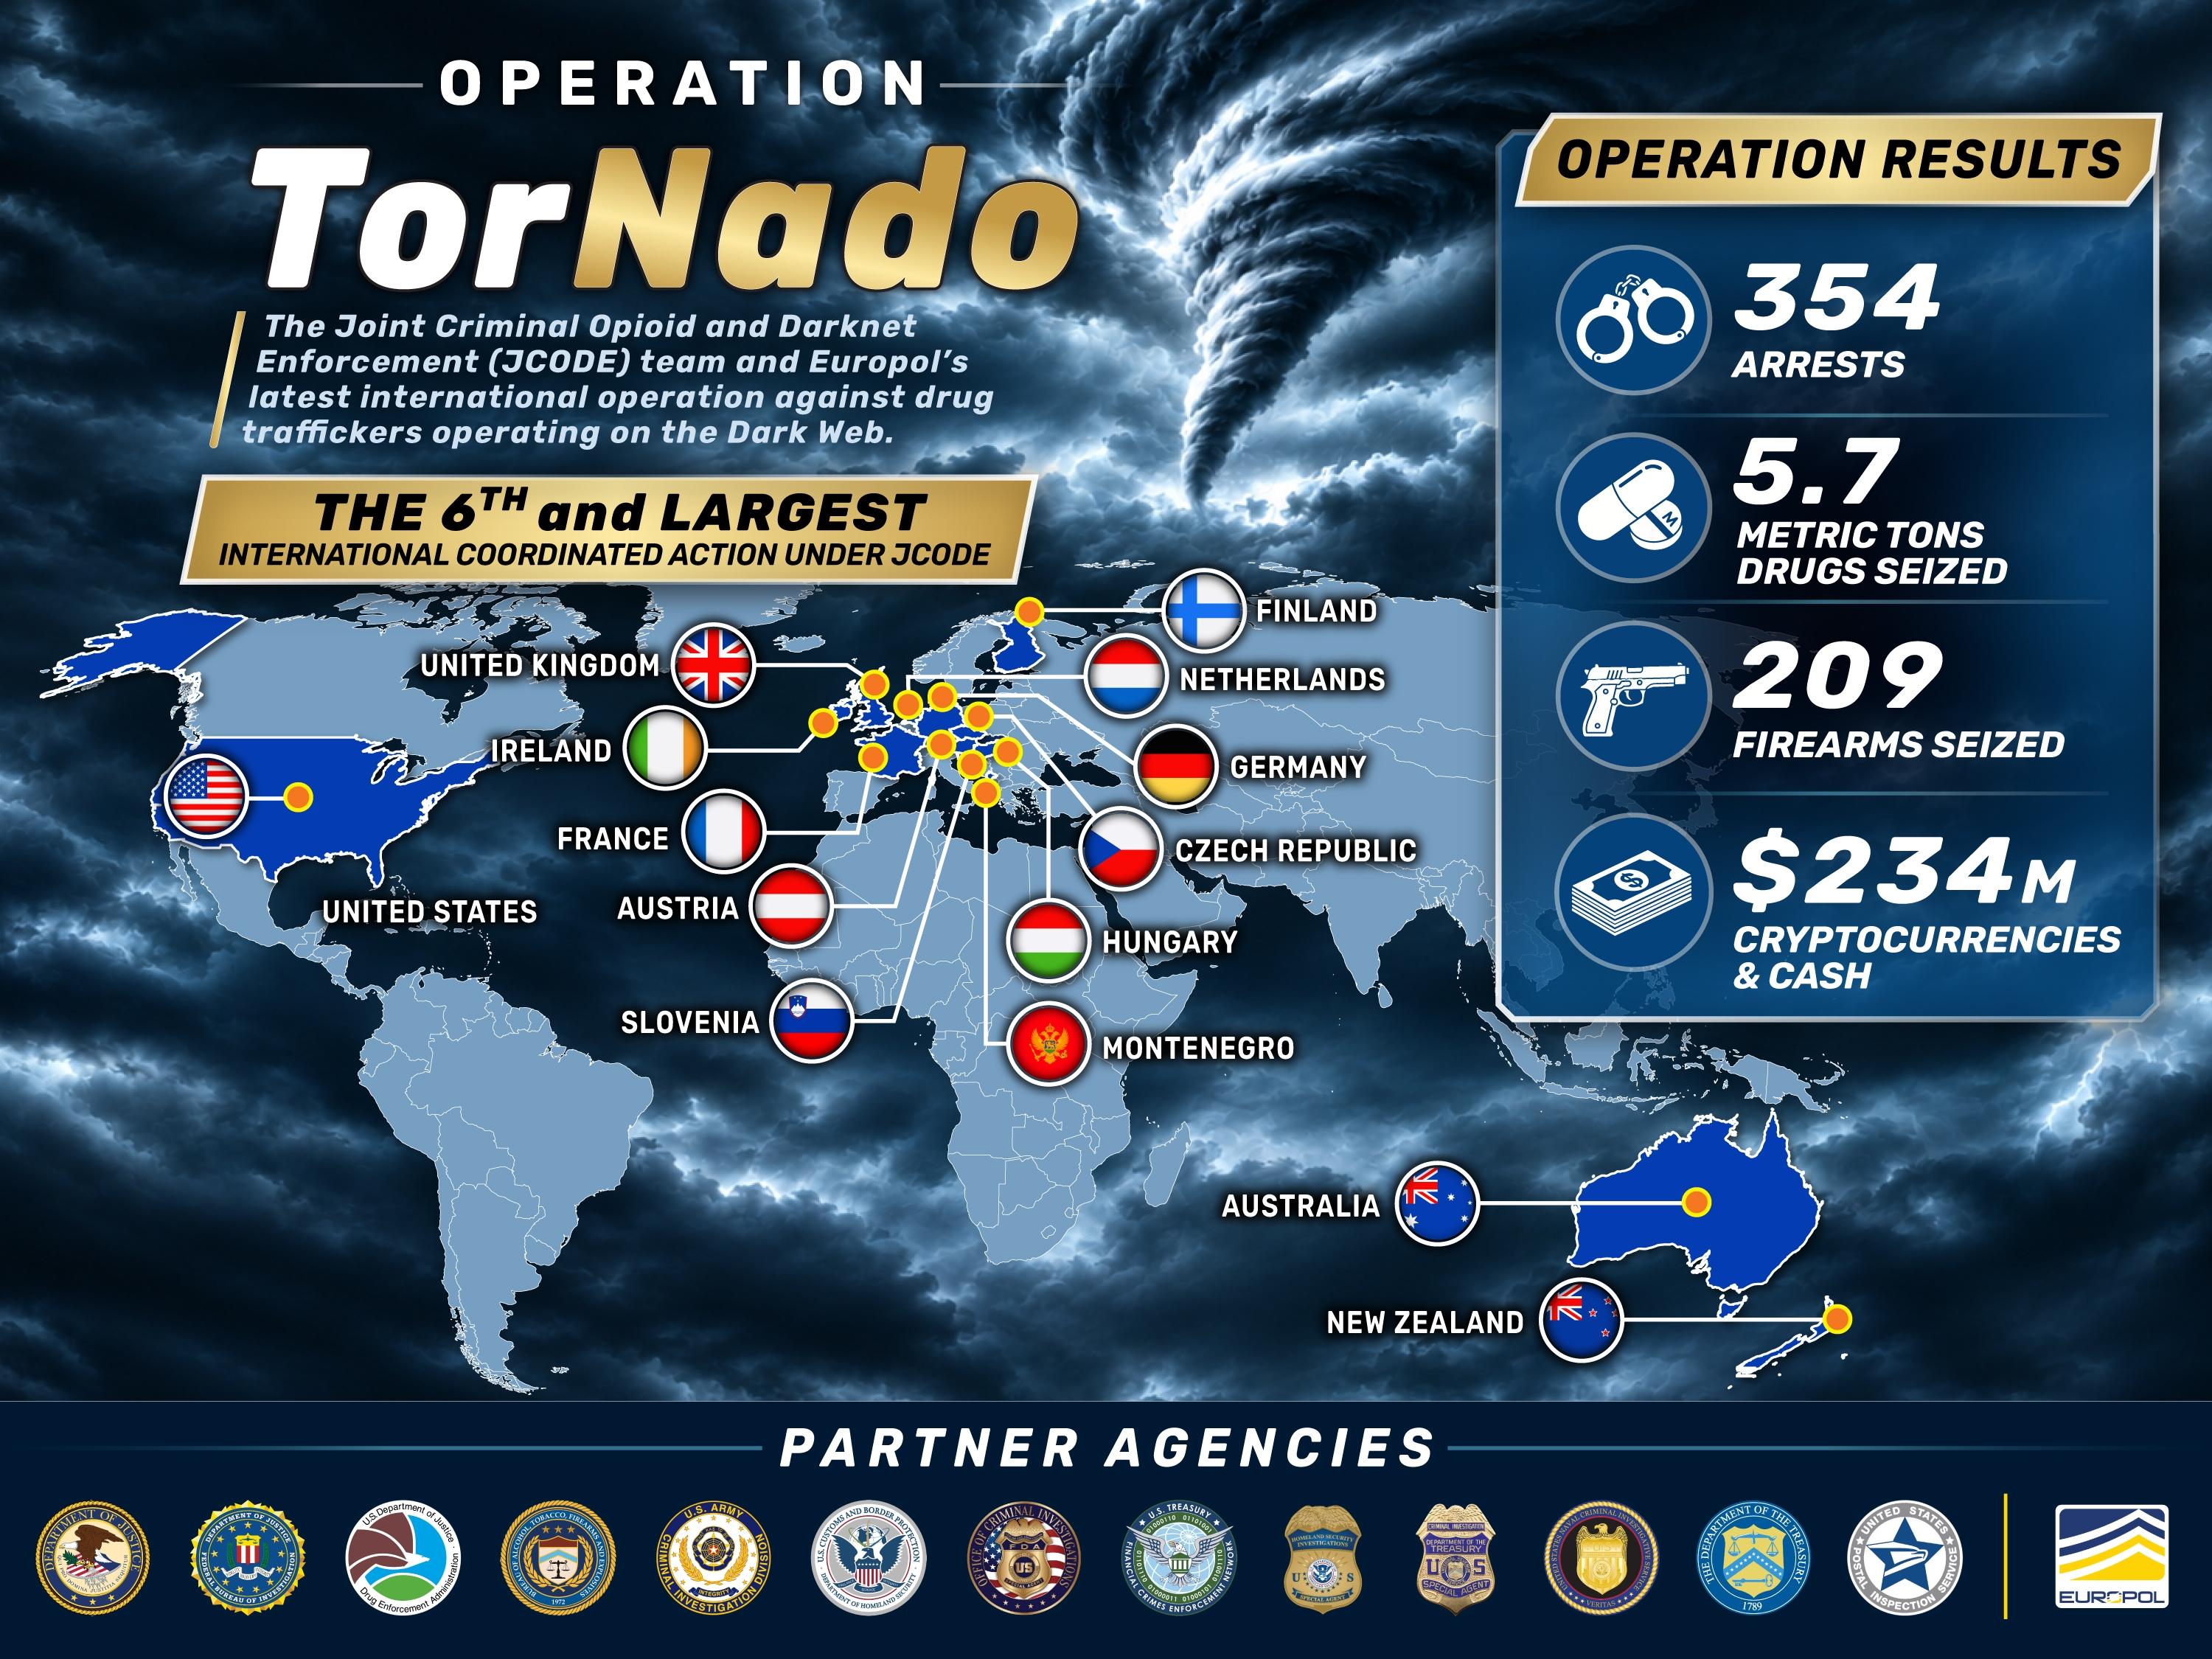
🚨 International law enforcement operation leads to 354 arrests and $234 million seized in massive dark web drug trafficking crackdown

The U.S. Department of Justice and Europol have announced the results of Operation TorNado, the largest coordinated takedown of dark web drug traffickers in JCODE's history, spanning the United States, Europe, Australia, and New Zealand.

Authorities arrested 354 suspects, including 132 in the United States, and seized more than $234 million in cash and cryptocurrency, 5.7 metric tons of drugs, 209 firearms, and 38 pill presses.

The operation targeted vendors and buyers operating across major darknet marketplaces, including Archetyp, Bohemia, Nemesis, Kingdom, Tor2Door, and DrugHub. Investigators used intelligence recovered from previously dismantled marketplaces to identify individuals behind anonymous vendor accounts.

Investigations remain ongoing, with additional suspects still being identified.

Source: https://www.justice.gov/opa/pr/international-law-enforcement-operation-targeting-opioid-and-fentanyl-traffickers-dark-web

Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee
Dark Web Informer :verified_paw: profile picture
🚨 Critical Apache HTTP Server flaw discovered by Anthropic and Google could allow hackers to execute code without authentication; CVE-2026-119618

The Apache Software Foundation has released an urgent security update addressing a critical remote code execution vulnerability in Apache HTTP Server's HTTP/2 module.

The flaw, tracked as CVE-2026-119618, involves a race condition that could allow unauthenticated attackers to corrupt server memory and potentially execute malicious code on vulnerable systems.

The vulnerability was independently discovered by Anthropic's AI-powered OSS Scanner and researchers at Google Cloud.

Apache HTTP Server versions 2.4.55 through 2.4.70 are affected, with version 2.4.71 released to address the issue.

Source: https://httpd.apache.org/security/vulnerabilities_24

No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee
Dark Web Informer :verified_paw: profile picture
🚨 Public exploit released for critical Cisco Expressway flaw allowing attackers to gain root access without authentication; CVE-2026-76466

https://github.com/dinosn/cve-2026-76466

A public proof-of-concept (PoC) exploit has been released for a critical Cisco Expressway vulnerability that could allow unauthenticated attackers to execute commands with root privileges on affected systems.

Tracked as CVE-2026-76466 (CVSS 9.8), the flaw involves hard-coded authentication credentials and insufficient certificate validation in clustered Expressway deployments. Researchers have demonstrated successful exploitation, potentially giving attackers complete control of vulnerable servers.

Cisco has released security updates, with Expressway versions X15.5.3 and earlier requiring an upgrade to X15.5.20. No active exploitation has been confirmed.

Source: https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-vcs-static-cred-hr7EWZ8t

πŸ’₯ No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee
Dark Web Informer :verified_paw: profile picture
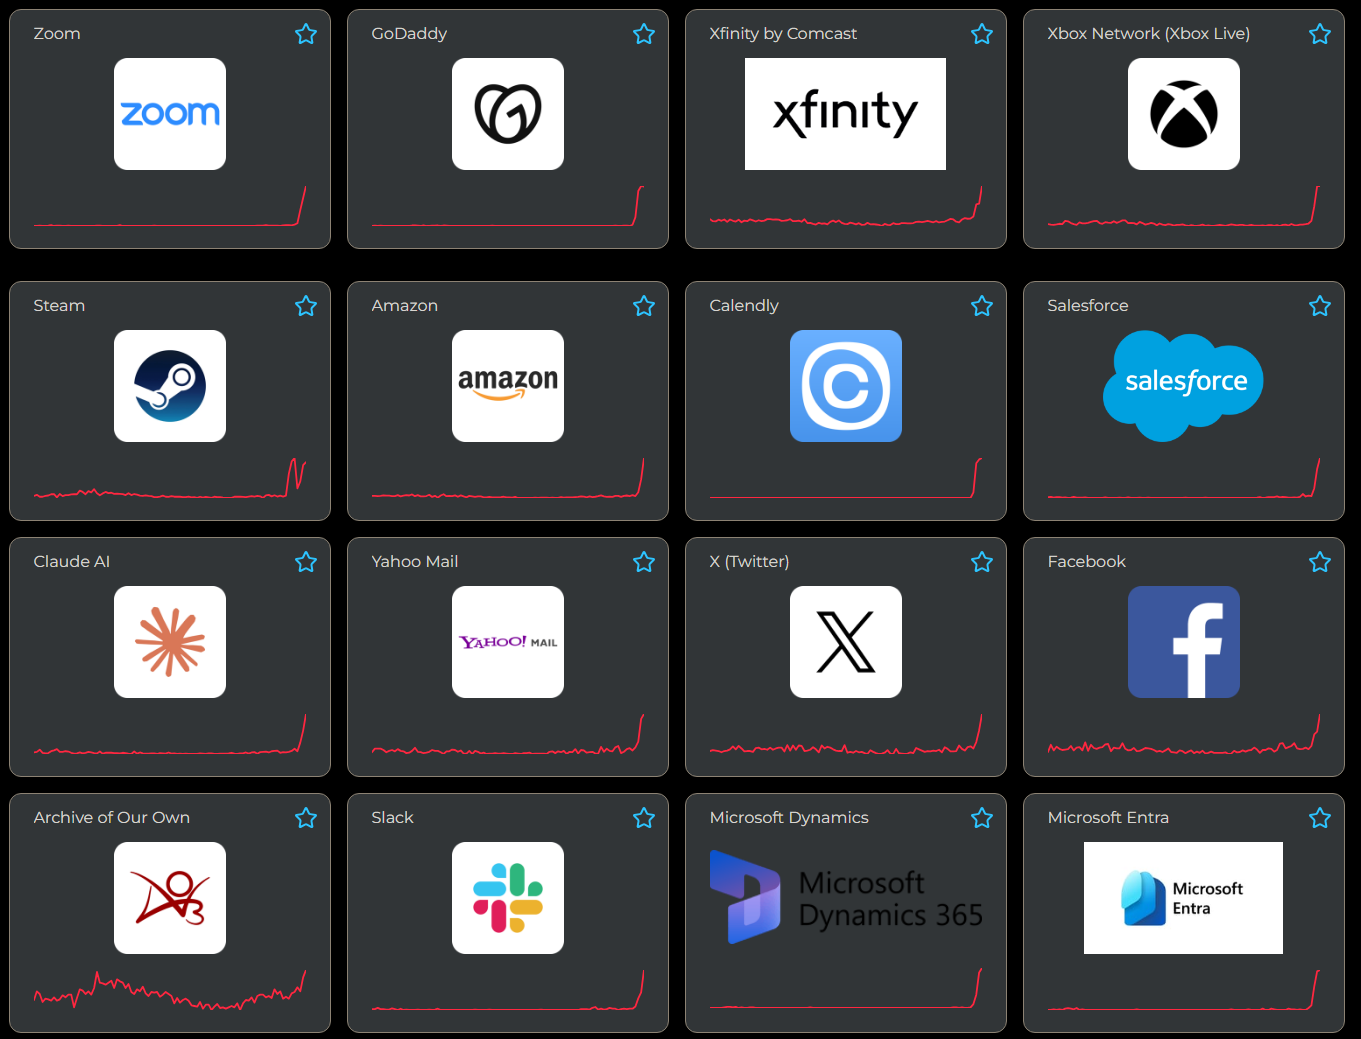
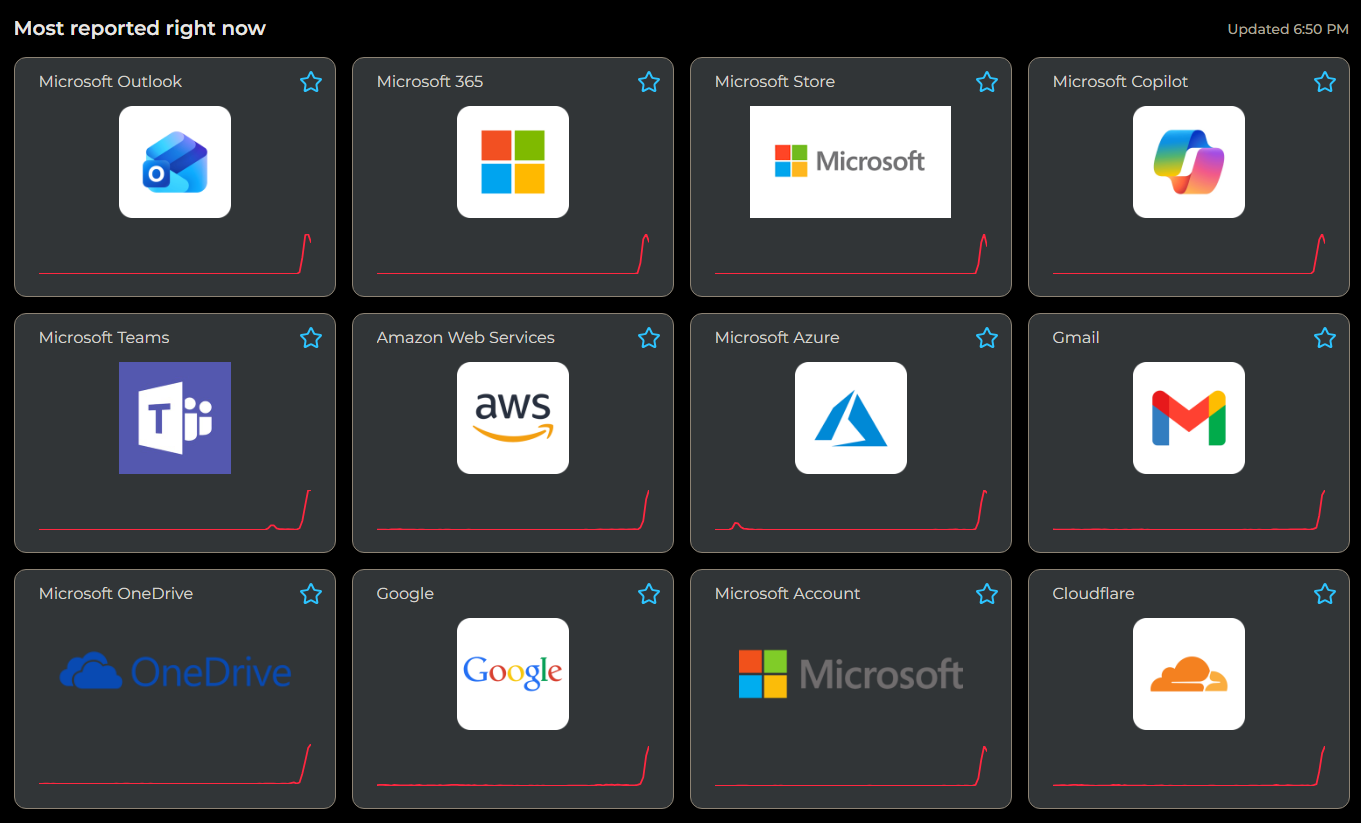
🚨 Many major services appear to be down or experiencing disruptions, with user reports spiking on Downdetector:

β€’ Microsoft Outlook
β€’ Microsoft 365
β€’ Microsoft Store
β€’ Microsoft Copilot
β€’ Microsoft Teams
β€’ Amazon Web Services (AWS)
β€’ Microsoft Azure
β€’ Gmail
β€’ Microsoft OneDrive
β€’ Google
β€’ Microsoft Account
β€’ Cloudflare
β€’ Zoom
β€’ GoDaddy
β€’ Xfinity
β€’ Xbox Network
β€’ Steam
β€’ Amazon
β€’ Calendly
β€’ Salesforce
β€’ Claude AI
β€’ Yahoo Mail
β€’ X (Twitter)
β€’ Facebook
β€’ Archive of Our Own
β€’ Slack
β€’ Microsoft Dynamics
β€’ Microsoft Entra

The scope and cause remain unclear.

πŸ’₯ Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee


1πŸ‘€1
Dark Web Informer :verified_paw: profile picture
‼️ New Dark Web Informer Blog Post!

Title: HomeMaison Data Sale Claim Lists 36.4 Million Records, 1.6M Emails and 330K Plaintext Passwords

Link: https://darkwebinformer.com/homemaison-data-sale-claim-lists-36-4-million-records-1-6m-emails-and-330k-plaintext-passwords/

πŸ’₯ Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
Dark Web Informer :verified_paw: profile picture
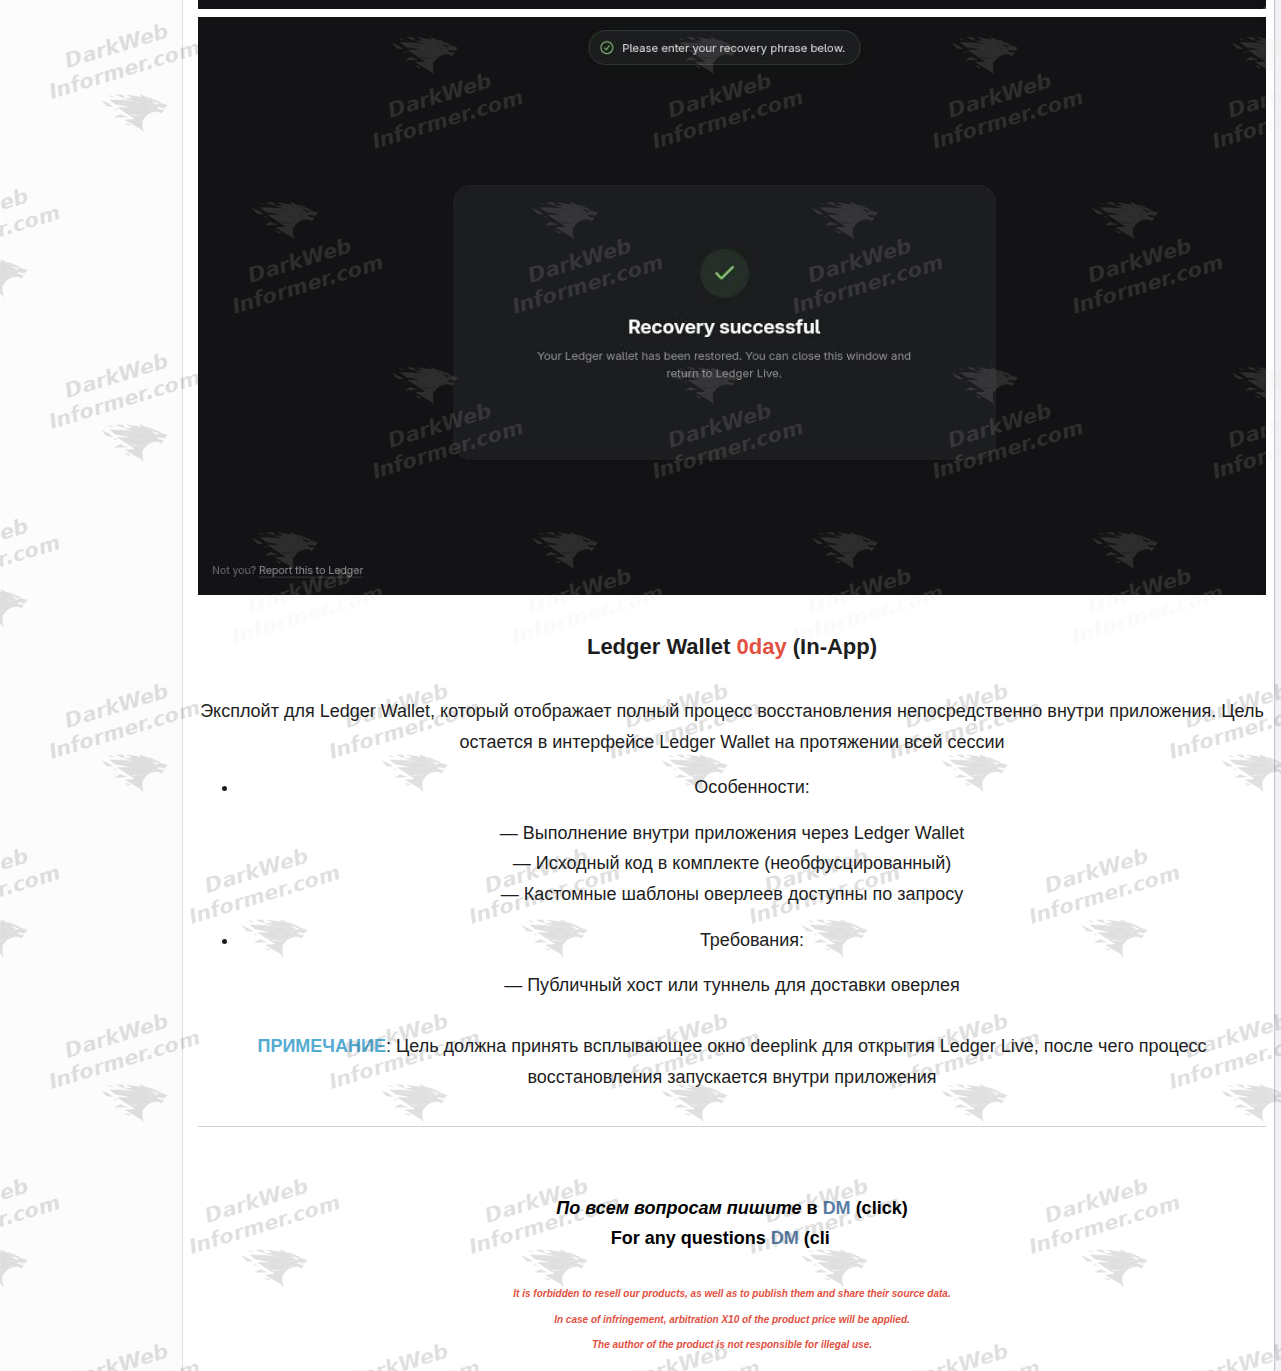
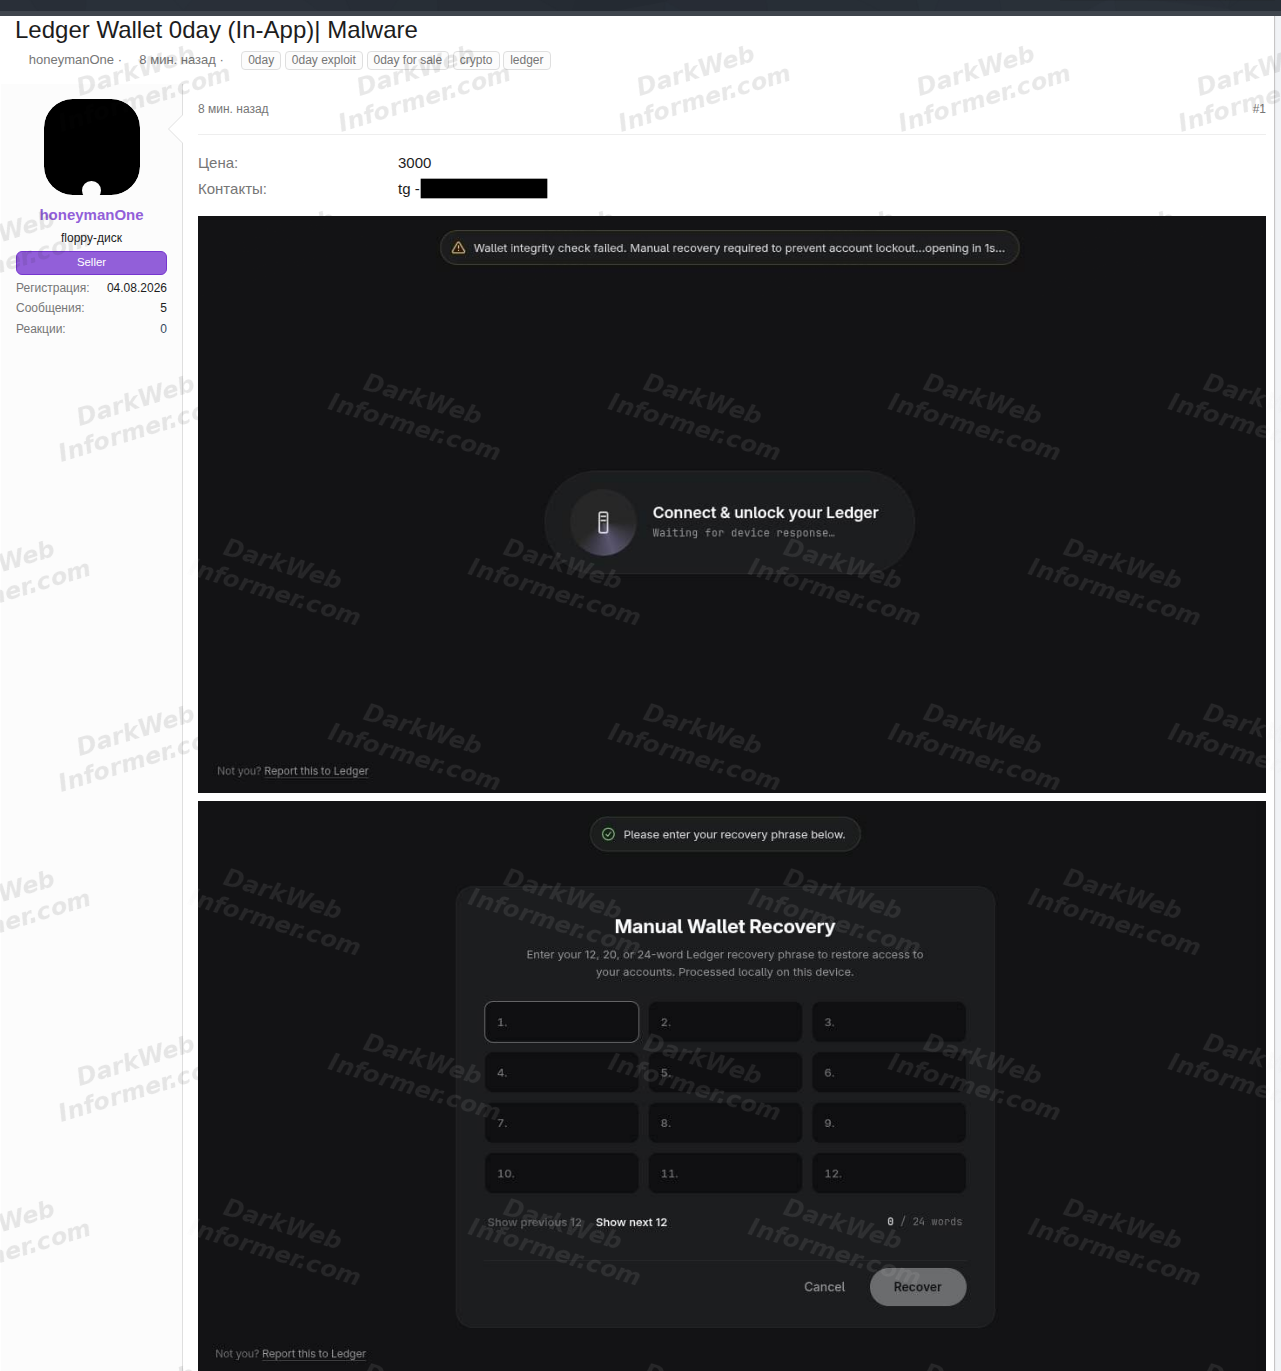
🚨 Ledger Live zero-day exploit allegedly offered for $3,000, targeting cryptocurrency recovery phrases

An actor using the handle "honeymanOne" is selling a tool claimed to exploit Ledger Live by displaying a fraudulent wallet recovery process inside the application.

The advertised attack uses a fake wallet integrity warning to trick users into entering their 12, 20, or 24-word recovery phrase.

Features include:

β€’ Fake in-app wallet recovery prompts
β€’ Customizable phishing overlays
β€’ Deep-link-based activation
β€’ Simulated recovery success messages
β€’ Source code included

The seller claims the attack remains within the Ledger Live interface, making the phishing attempt appear legitimate.

Claim is currently unverified. No genuine Ledger Live zero-day vulnerability has been demonstrated.

πŸ’₯ Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing

Need API access? darkwebinformer.com/api-details

Check out the Telegram channel: t.me/SliceForLifeee