Damus
Dark Web Informer :verified_paw: profile picture
Dark Web Informer :verified_paw:
@Dark Web Informer :verified_paw:

Website: https://darkwebinformer.com

Website Pricing (Crypto payments are fully automated): https://darkwebinformer.com/pricing

Socials: https://darkwebinformer.com/socials

API Access: https://darkwebinformer.com/api-details

About Dark Web Informer: https://darkwebinformer.com/about-dark-web-informer

X: https://x.com/DarkWebInformer

Updated: 2026-07-20

Relays (1)
  • wss://relay.ditto.pub – read & write

Recent Notes

Dark Web Informer :verified_paw: profile picture
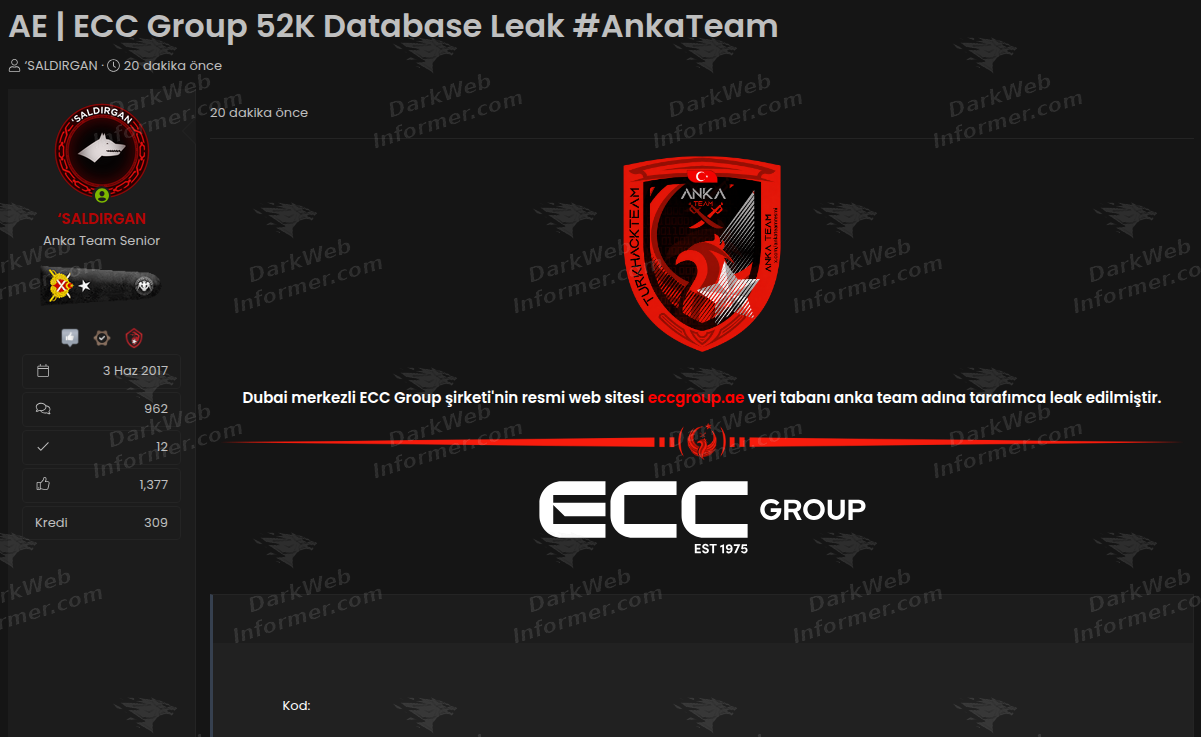
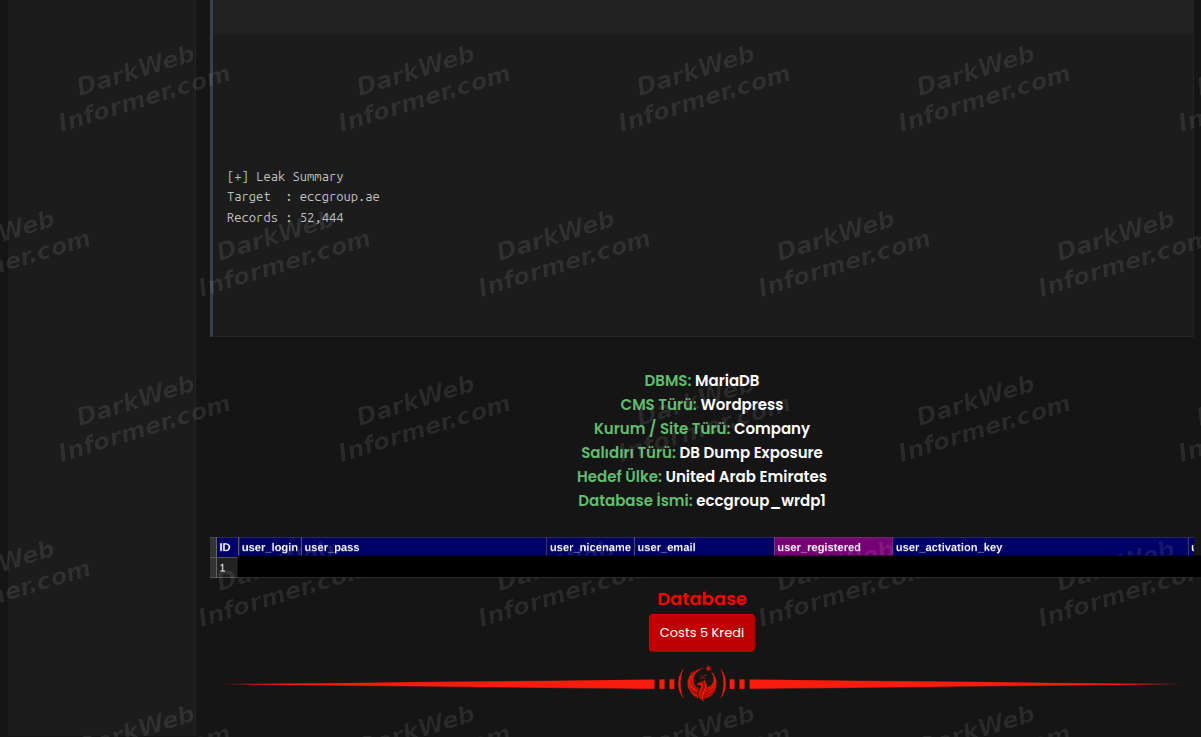
🚨🇦🇪 ECC Group database containing 52K+ records allegedly leaked by AnkaTeam

ECC Group is a Dubai-based group of companies operating across construction, engineering, fit-out, manufacturing, building materials, facilities, and real estate development.

An actor using the handle SALDIRGAN, identifying with AnkaTeam, claims to have leaked a database associated with ECC Group’s official website.

Claimed exposed data includes:

• 52,444 database records
• WordPress user accounts
• Usernames and display names
• Email addresses
• Password hashes
• User registration dates
• Account activation data
• Other WordPress database records

The actor identifies the backend as MariaDB and the affected CMS as WordPress, describing the incident as a database dump exposure. A sample administrator record was published alongside the claim.

The breach claim, record count, and full scope of the exposed data have not been independently verified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Dark Web Informer :verified_paw: profile picture
🚨 GitLab CVSS 10 vulnerability exploited just one day after disclosure

Threat actors have begun exploiting CVE-2026-85706, a critical path traversal vulnerability affecting self-hosted GitLab Community and Enterprise Edition instances.

The flaw allows an unauthenticated attacker to read arbitrary files from a vulnerable GitLab server using a single HTTP request.

Affected versions include:

• GitLab 18.7 through versions before 19.1.8
• GitLab 19.2 through versions before 19.2.6
• GitLab 19.3 through versions before 19.3.2

GitLab disclosed and patched the vulnerability on September 10.

Just one day later, watchTowr began observing in-the-wild exploitation attempts and warns that mass exploitation is likely to follow.

Administrators should upgrade immediately to GitLab 19.1.8, 19.2.6, 19.3.2, or a newer supported release.

GitLab.com is already patched.

Source: https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-3-2-released/

Dark Web Informer :verified_paw: profile picture
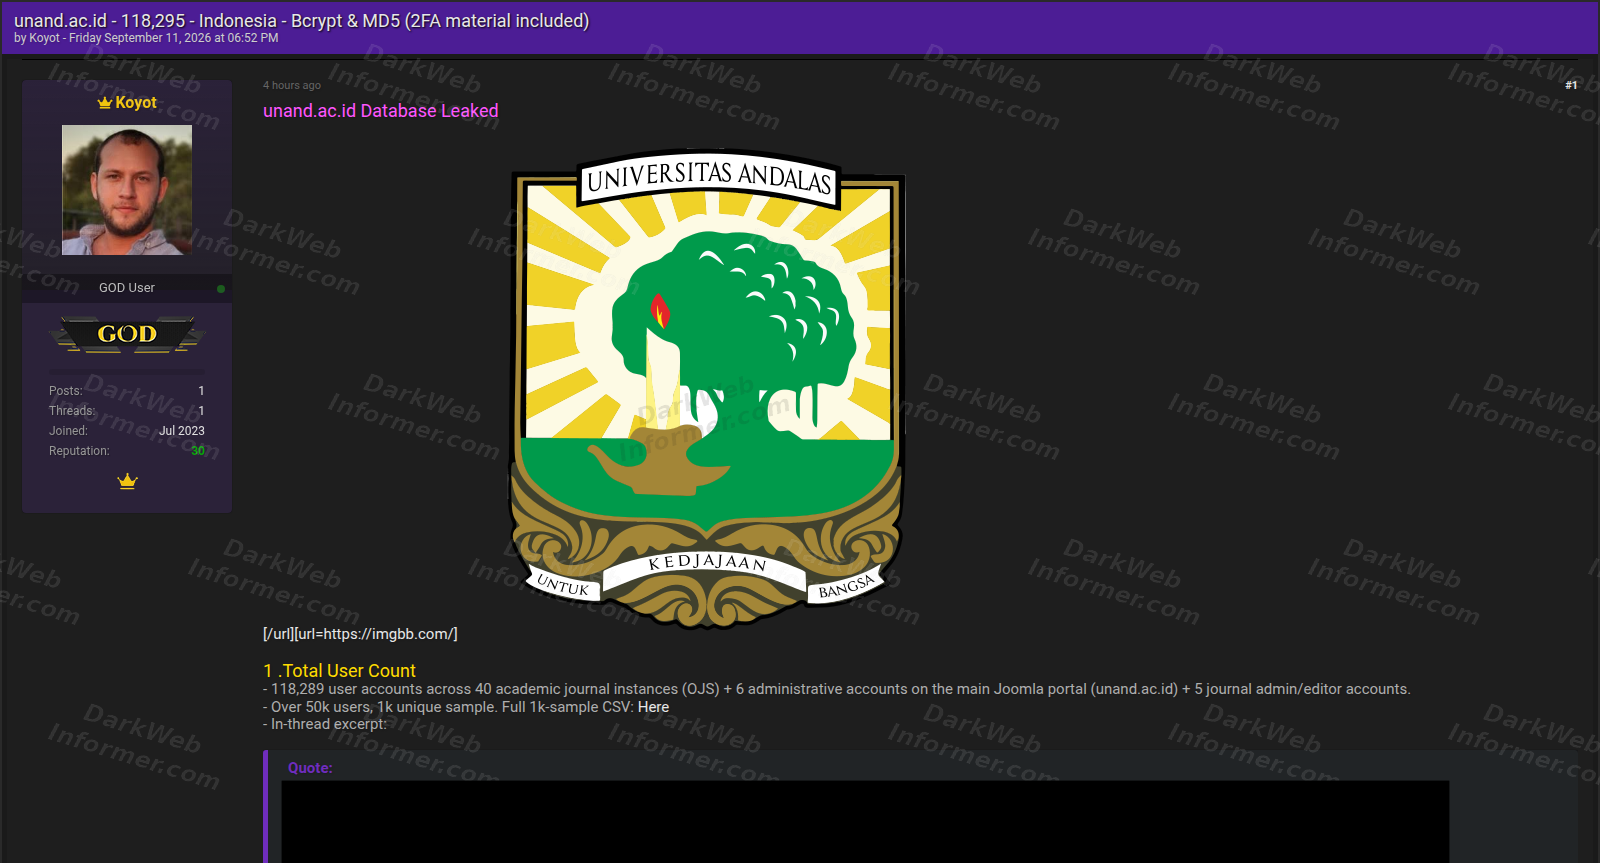
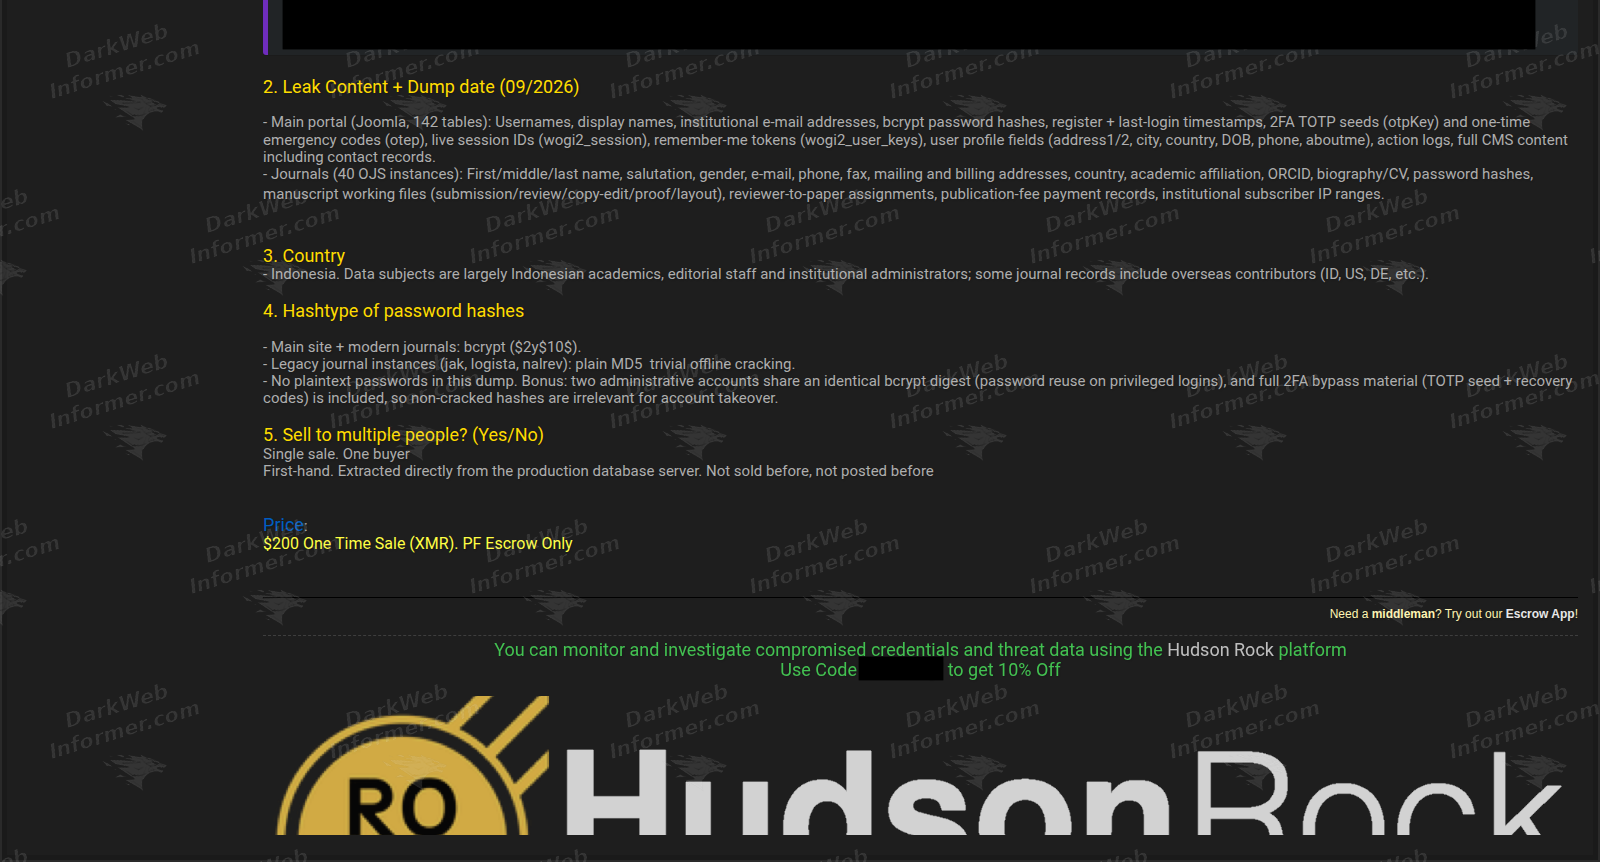
🚨🇮🇩 Universitas Andalas dataset containing 118K+ accounts allegedly leaked

Universitas Andalas is a public university in Padang, West Sumatra, Indonesia, operating academic, administrative, and research systems including numerous online journal platforms.

A forum actor using the handle Koyot claims to have obtained data covering 118,289 user accounts across 40 academic journal instances, along with administrative accounts tied to the university’s main Joomla portal and journal systems.

Claimed exposed data includes:

• Usernames and display names
• Institutional email addresses
• bcrypt and MD5 password hashes
• Registration and last-login timestamps
• TOTP 2FA seeds and emergency recovery codes
• Active session IDs and remember-me tokens
• Names, dates of birth, phone numbers, and addresses
• Academic affiliations and ORCID identifiers
• Biographies and CV information
• Manuscript and peer-review working files
• Reviewer assignments
• Publication-fee payment records
• Institutional subscriber IP ranges
• Administrative and CMS records

The actor claims the dump was extracted in September 2026 and includes data from the university’s main portal and 40 Open Journal Systems instances. A sample of the purported records was published with the listing.

The dataset is being offered as a single sale for $200 in XMR, with escrow reportedly accepted.

The breach claim, record count, authenticity of the data, and claimed exposure of 2FA material have not been independently verified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing


Dark Web Informer :verified_paw: profile picture
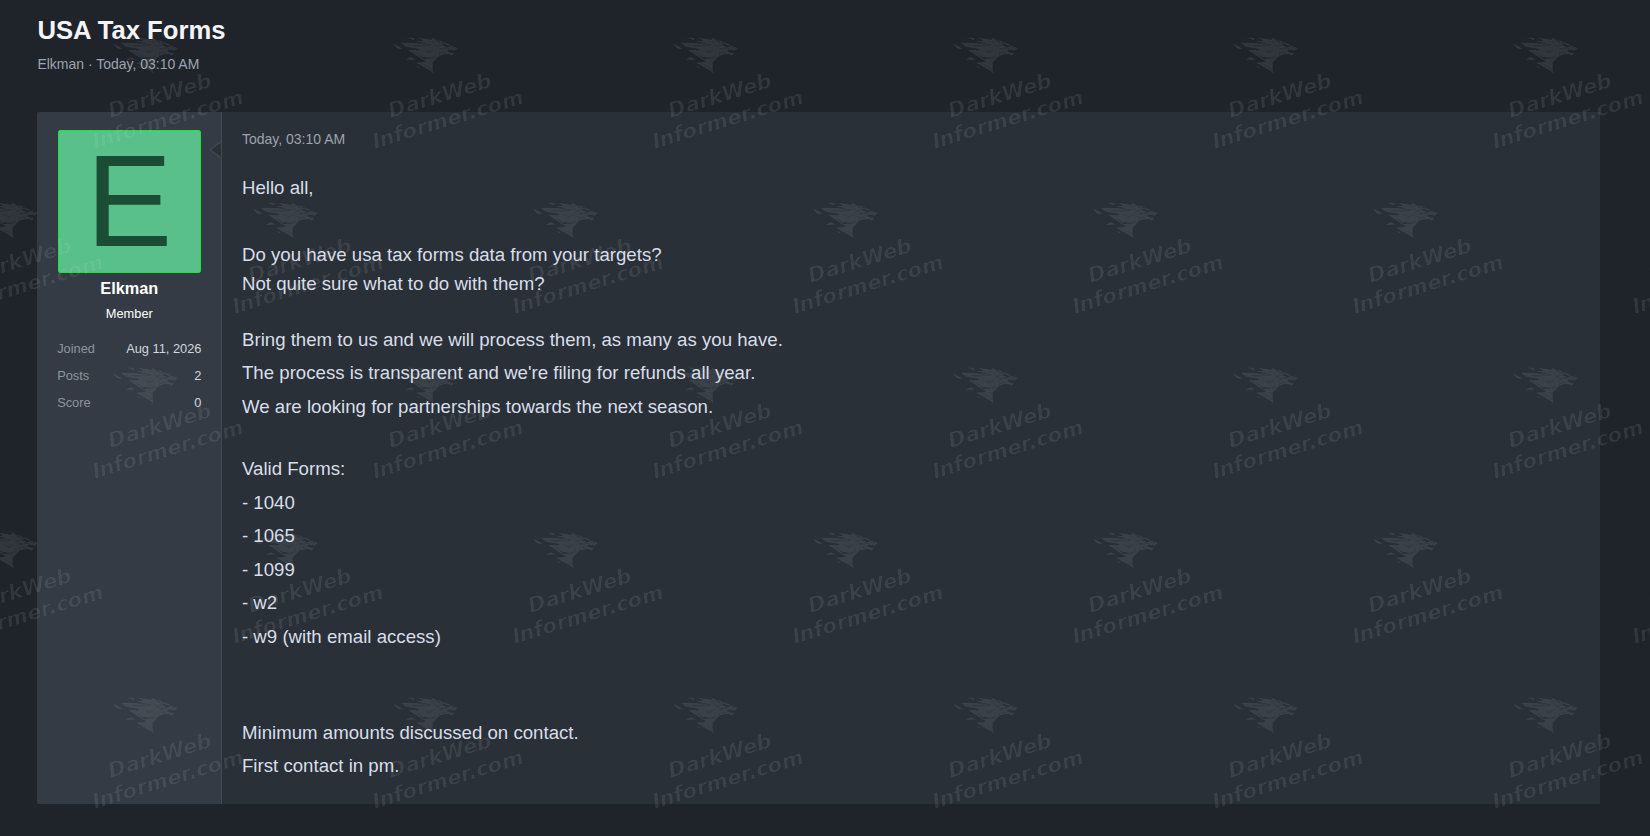
🚨🇺🇸 Forum actor solicits U.S. tax forms for refund filing operation

U.S. tax forms such as 1040s, 1065s, 1099s, W-2s, and W-9s can contain sensitive taxpayer, income, employment, and business information used for federal tax reporting.

A forum actor using the handle Elkmann is seeking partners who can provide tax-form data from compromised targets, claiming they can process the information and file for refunds throughout the year.

Forms being requested include:

• Form 1040 individual tax returns
• Form 1065 partnership returns
• Form 1099 information returns
• W-2 wage and tax statements
• W-9 taxpayer identification forms
• W-9 records accompanied by email access

The actor states they can process as many forms as partners can provide and is actively seeking partnerships ahead of the next tax season.

Minimum quantities are reportedly discussed privately, with initial contact requested through forum messages.

The legitimacy, scale, and success of the claimed refund operation have not been independently verified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Dark Web Informer :verified_paw: profile picture
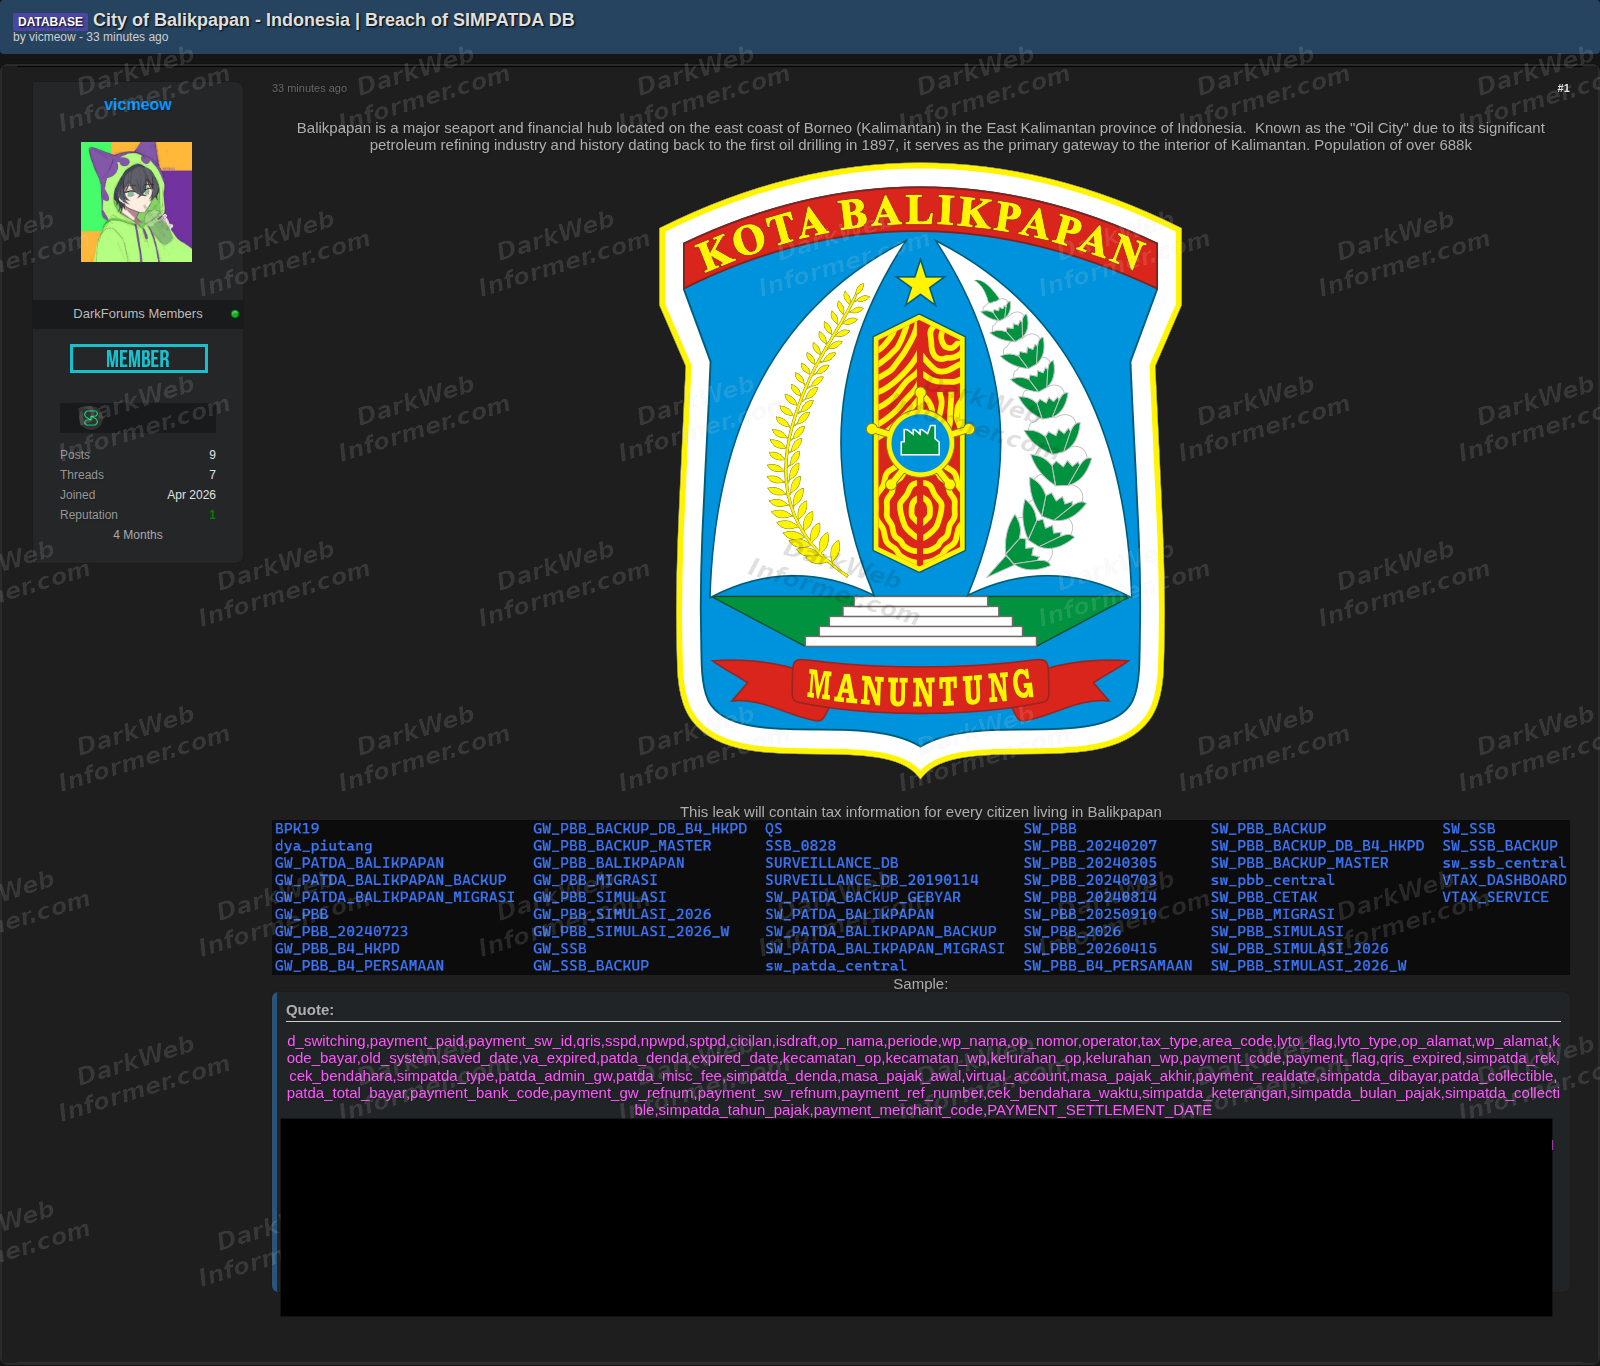
🚨🇮🇩 City of Balikpapan SIMPATDA database allegedly breached

Balikpapan is a major city in East Kalimantan, Indonesia, whose municipal government manages local public services, taxation, and regional administration.

A cybercrime forum actor using the handle vicmeow claims to have breached a SIMPATDA database, a system associated with managing local government revenue and taxation data.

Claimed exposed data includes:

• Resident and taxpayer information
• Tax identification and payment records
• Names and addresses
• Billing and payment status
• Tax periods and due dates
• Property and land-related records
• Administrative and operator information
• Multiple database backups and internal tables

The actor claims the leak contains tax information for residents of Balikpapan and published a downloadable archive along with sample database records.

The breach claim, source of the data, and full scope of the exposure have not been independently verified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Dark Web Informer :verified_paw: profile picture
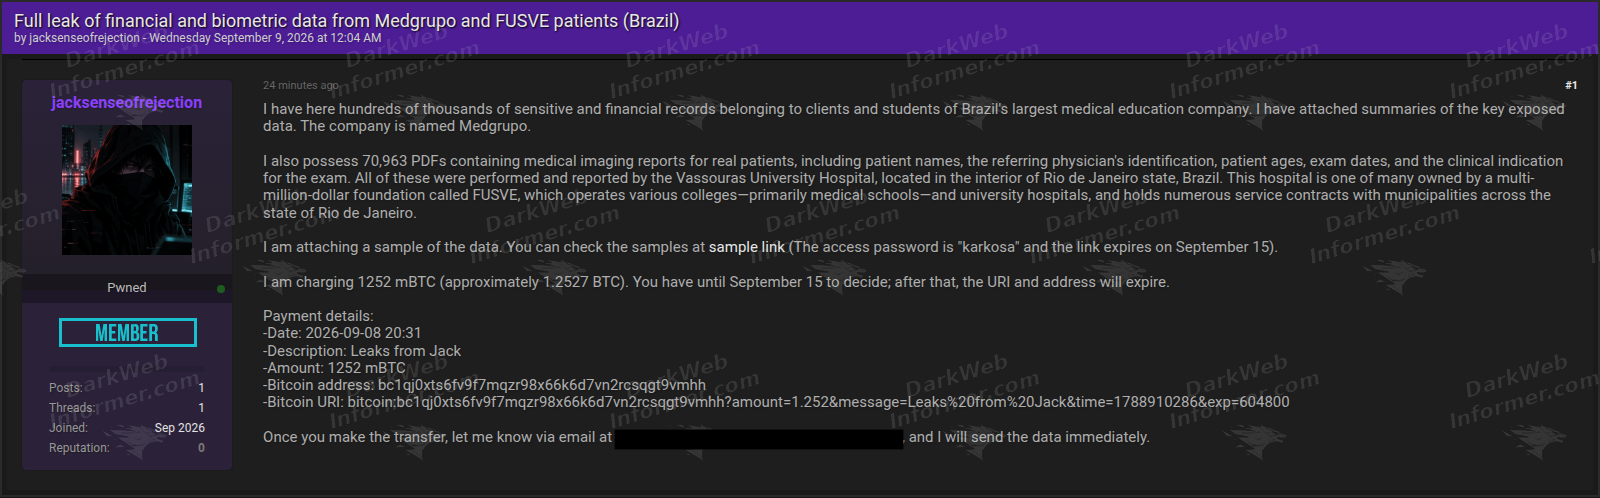
🚨🇧🇷 Medgrupo and FUSVE patient data allegedly leaked and offered on a cybercrime forum

Medgrupo is a Brazilian medical education company, while FUSVE operates educational and healthcare institutions in Rio de Janeiro state, including Vassouras University Hospital.

A threat actor using the handle jacksenseofrejection claims to possess hundreds of thousands of sensitive and financial records associated with Medgrupo clients and students, along with 70,963 PDF medical imaging reports involving patients of Vassouras University Hospital.

Claimed exposed data includes:

• Client and student financial records
• Patient names
• Patient ages
• Referring physician information
• Medical imaging reports
• Examination dates
• Clinical indications
• Other sensitive medical information

The actor published samples and is asking approximately 1.25 BTC for the purported data, with an offer deadline of September 15, 2026.

The breach claim, origin of the data, and full scope of the exposure have not been independently verified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing