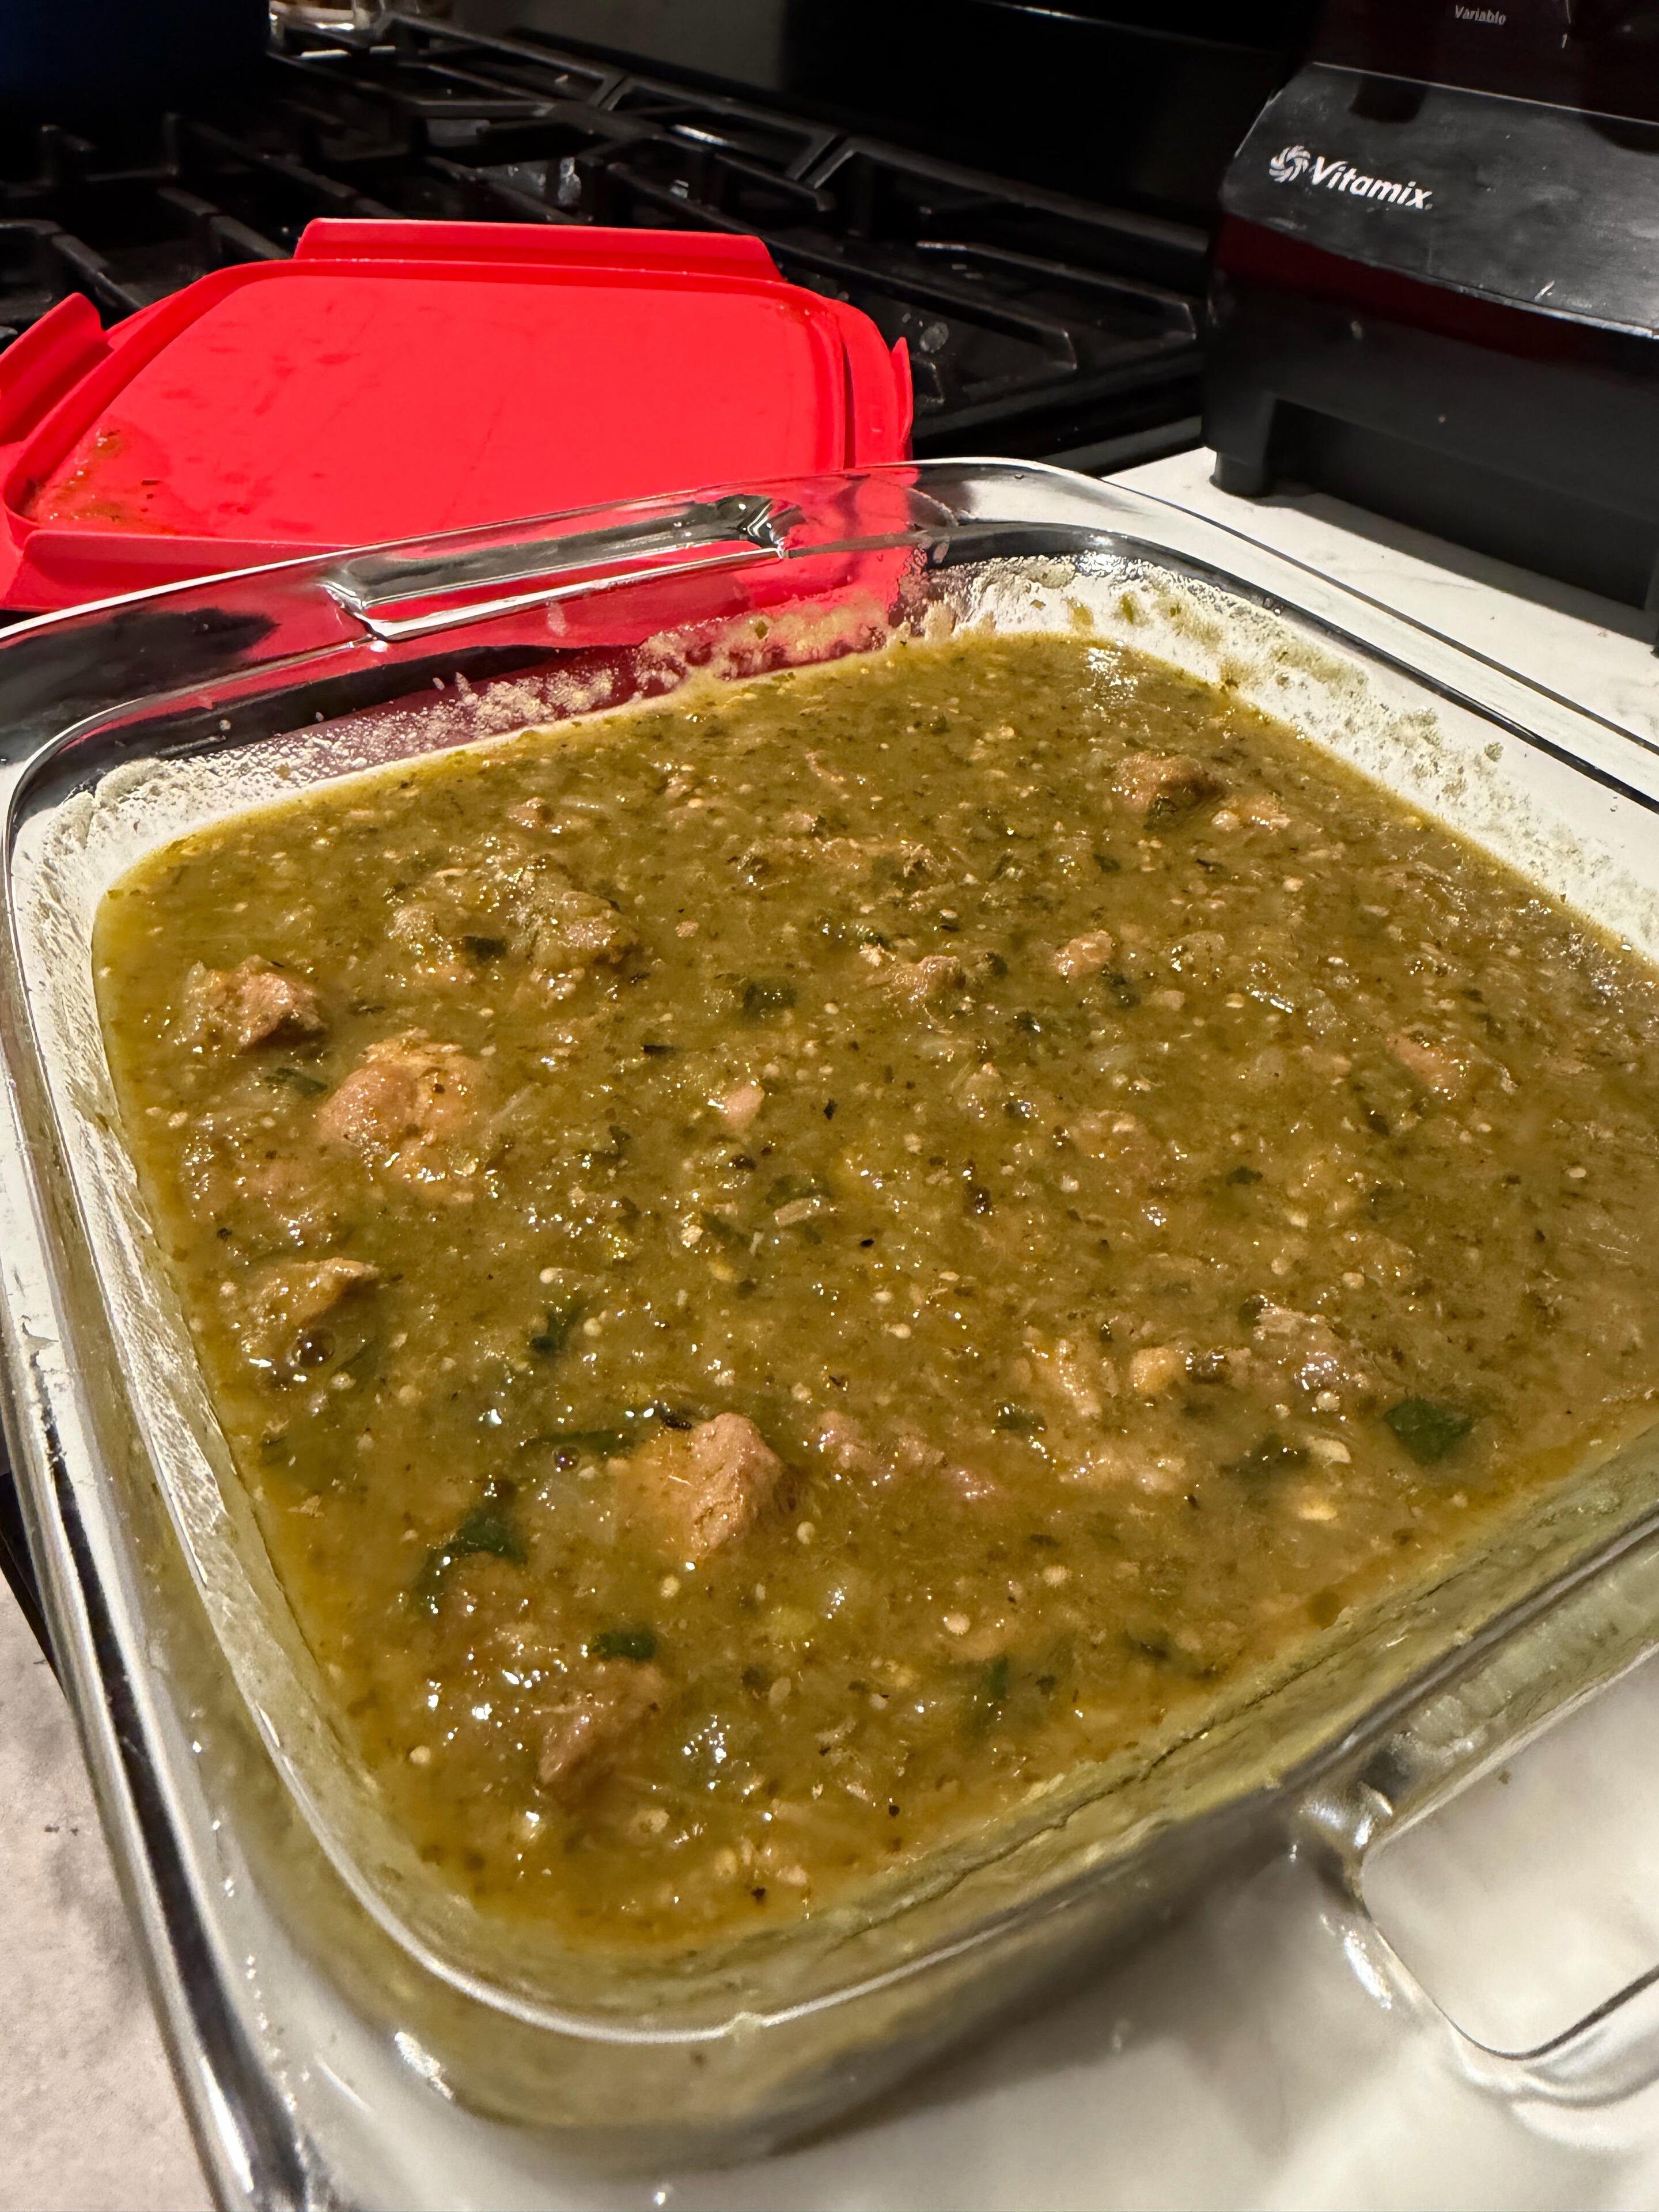
Not the best picture, but the pork green chile tonight did no disappoint. Local pork, peppers, and tomatillos. Can’t believe I haven’t made this before.
I’ve been sleeping on jj (jujitsu) for too long. Today I asked my agents which they would prefer to use if working alone and all of them said jj but making sure it stayed git compatible.
I’m going to ask them to start working this way so I can learn. Excited to see if they are more efficient with my PRs
I try not to post links to X but some of the items in this list show you how powerful it could be. I also tested it briefly for flexible incoming structured data validation and it worked well. Long story short, anywhere you might consider a customer trained classifier to avoid an LLM call is a use-case for Jev.
I submitted for the waitlist and was surprised I got an invite pretty quick. Ran a few tests this morning and it seems like there are going to be a ton of ways to use it. Amazing how cheap it is and the agent was able to wire up quick tests on its own
Despite all the hype this has been getting on X, I actually think people might not understand how big of a deal it is. They refer to it as a system one model, but I think a better name is a general classifier.
Jev replace specialized machine learning models out of the box in many ways. May of the inefficiencies in current agent workflows like model selection or memory management can be improved. This is going to supercharge the speed and efficiency of agentic workflows and completely shift how AI and data analytics interact.
I pulled it into my agent this morning and had an improved proof of concept data validation workflow for a project I had been working on for years within 10 minutes. All the testing I did this morning over the course of a few hours cost me < 3 cents. Checking a 22k record database for errors (without needing to explicitly define failure criteria) might cost $1.50.
It’s gotta be something that could run locally right? The cost is so low. Or is it still a big model just with sparse cheap throughput? This is where I don’t know enough yet…
I would argue it’s always safer. A passphrase is either short enough to remember and likely easy to brute force OR long and secure and your single point of failure to lose your funds when you can’t reproduce it. Or your trust a password manager, which is maybe okay as long as you have a back up plan for that too.
You should talk to Keith from seed signer about entropy. He has been putting in the work including showing why dice rolls aren’t that “risky”
I’m unconvinced anyone should ever use a passphrase - should never be compared to multisig.
The single sig focused hardware marketing budgets will always try to convince you otherwise. I have no regrets in trusting level headed research from open source and DIY devs over corporate marketing.