Damus

Recent Notes

Thomas Roccia :verified: profile picture
πŸ€“ I was early but that doesn’t mean much!

I just released my latest newsletter, where I reflect on the work I have been doing around AI and threat intelligence over the past four years.

It is more of a personal reflection on the things I built, the ideas I explored, what worked, what didn’t, and what I learned along the way πŸ‘‡

https://newsletter.securitybreak.io/campaign/e75962cd-6b81-4139-94f2-f24da7effa22/f4ed8625-e503-4269-a37a-85500fc90092
Thomas Roccia :verified: profile picture
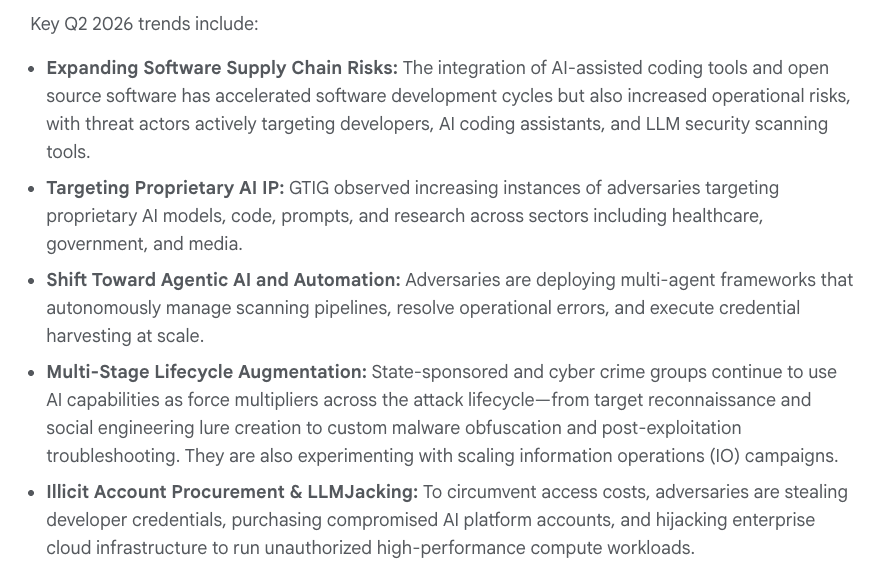
🧐 If you missed them, GTIG and Anthropic just released two new reports on AI abuse!

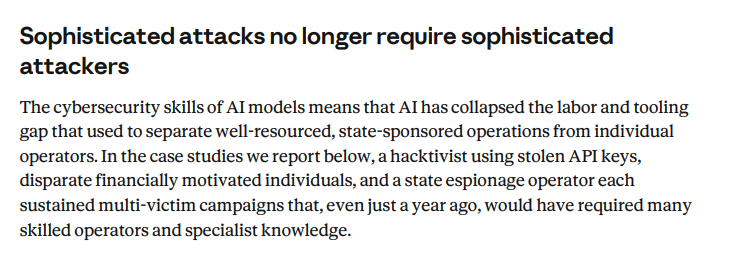
Sophisticated attacks are not anymore a reliable criteria to define the threat actor behind them because the gap between script kiddies and nation-state actors keeps shrinking.

Agentic workflows connected to offensive tools can handle recon, exploitation, exfiltration, translation, targeting and capability development with far less expertise than before.

Your stolen API keys and session tokens are more than ever a juicy target for attackers. They can resell them, power underground services billed on you, use them for attribution laundering and access agents.

Anthropic report shows AI usage on surveillance, large-scale social media analysis, live translation and operator support.

GTIG shows how attackers targets coding agents, MCP servers, agent configuration and AI security systems themselves.

We’ve been observing attackers targeting the AI ecosystem for a while. Now it is accelerating!

There is a lot to unpack from those reports!

Thomas Roccia :verified: profile picture
🧐 When attackers expose their LLM interface, they expose part of their infrastructure and potentially much more!

Unit 42 recently released a threat report that shows how a self hosted NextChat instance, SOCKS5 relays, scripts and reused certificates could be used as a pivot point in your threat research.

In a recent campaign they discovered an exposed NextChat interface used to interact with different models.

The hosted LLM provided all the information needed to extract the Active Directory database, but the infrastructure was accessible to anyone without authentication, exposing the attackers playbook, prompt history and malicious scripts.

Even threat actors are hiring rookies! πŸ˜…

Report: https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/

Gary Blosser · 77w
nostr:nprofile1qy2hwumn8ghj7un9d3shjtnddaehgu3wwp6kyqpqkvsn33t60mgm4hs5dghmkv87n8srzadugaez3twyhmrczs4wutssvme54t I have a soft spot for Pixar villain πŸ˜… https://media.infosec.exchange/infosec.exchange/media_attachments/files/114/232/196/760/347/895/original/12dc1ae10e604142.png