Damus

Recent Notes

Scott Leggett :fedi: :golang: · 6w
nostr:nprofile1qy2hwumn8ghj7un9d3shjtnyd968gmewwp6kyqpqmvfdung5whdgpwwllyqjggm5lrh4wylvjw3kgex9dxzcsjuc75fsgnuygl do Apple normally report vulnerabilities upstream in the open source software they ship?
Harry Sintonen profile picture
I recently discovered a command injection vulnerability (CWE-78) from Info-ZIP (zip). Advisory: https://sintonen.fi/advisories/infozip-test-option-command-injection.txt

The fix is now available in #Debian as DSA 6439-1: https://lists.debian.org/debian-security-announce/2026/msg00350.html

Other platforms shipping zip command should also pick up the patch: https://sources.debian.org/data/main/z/zip/3.0-16/debian/patches/fix-command-injection.patch

NOTE: macOS included zip command is not affected.

#advisory #vulnerabilityresearch #cybersecurity #infosec
1
Harry Sintonen · 6w
The reason #macOS zip command is not vulnerable is that #Apple fixed this issue years ago (in 2008) already: https://github.com/apple-oss-distributions/zip/blob/zip-11.1/zip/patch-Apple It is unclear why the fix didn't get reported upstream.
Harry Sintonen profile picture
It appears that AI companies target open source contributors with their marketing spam:

"we noticed you contributed to curl/curl — thanks for helping build open source. We're running a small program for Github OSS contributors and would love to invite you.

You'll receive $25 in XXXXXXXXX credits to use frontier AI models (this time YYYYY) through a single OpenAI-compatible endpoint."

#enshittification
Harry Sintonen · 21w
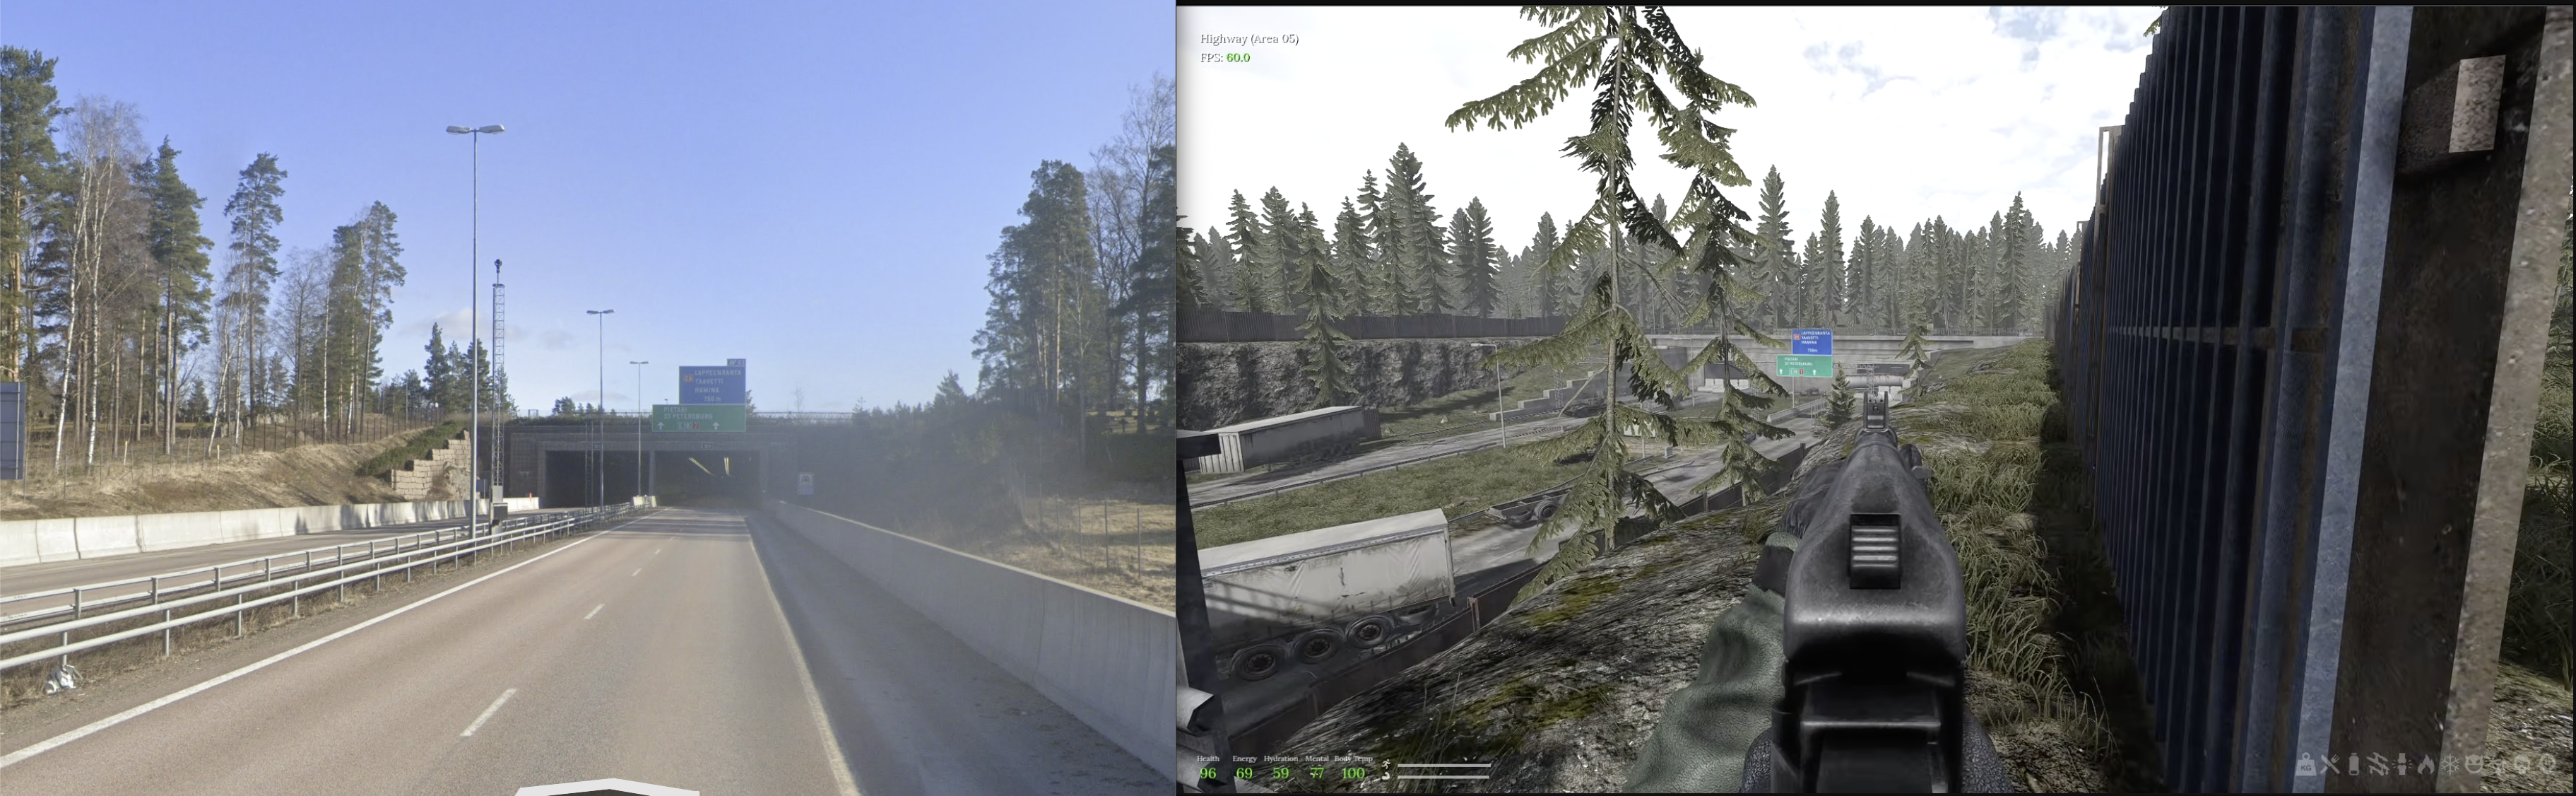
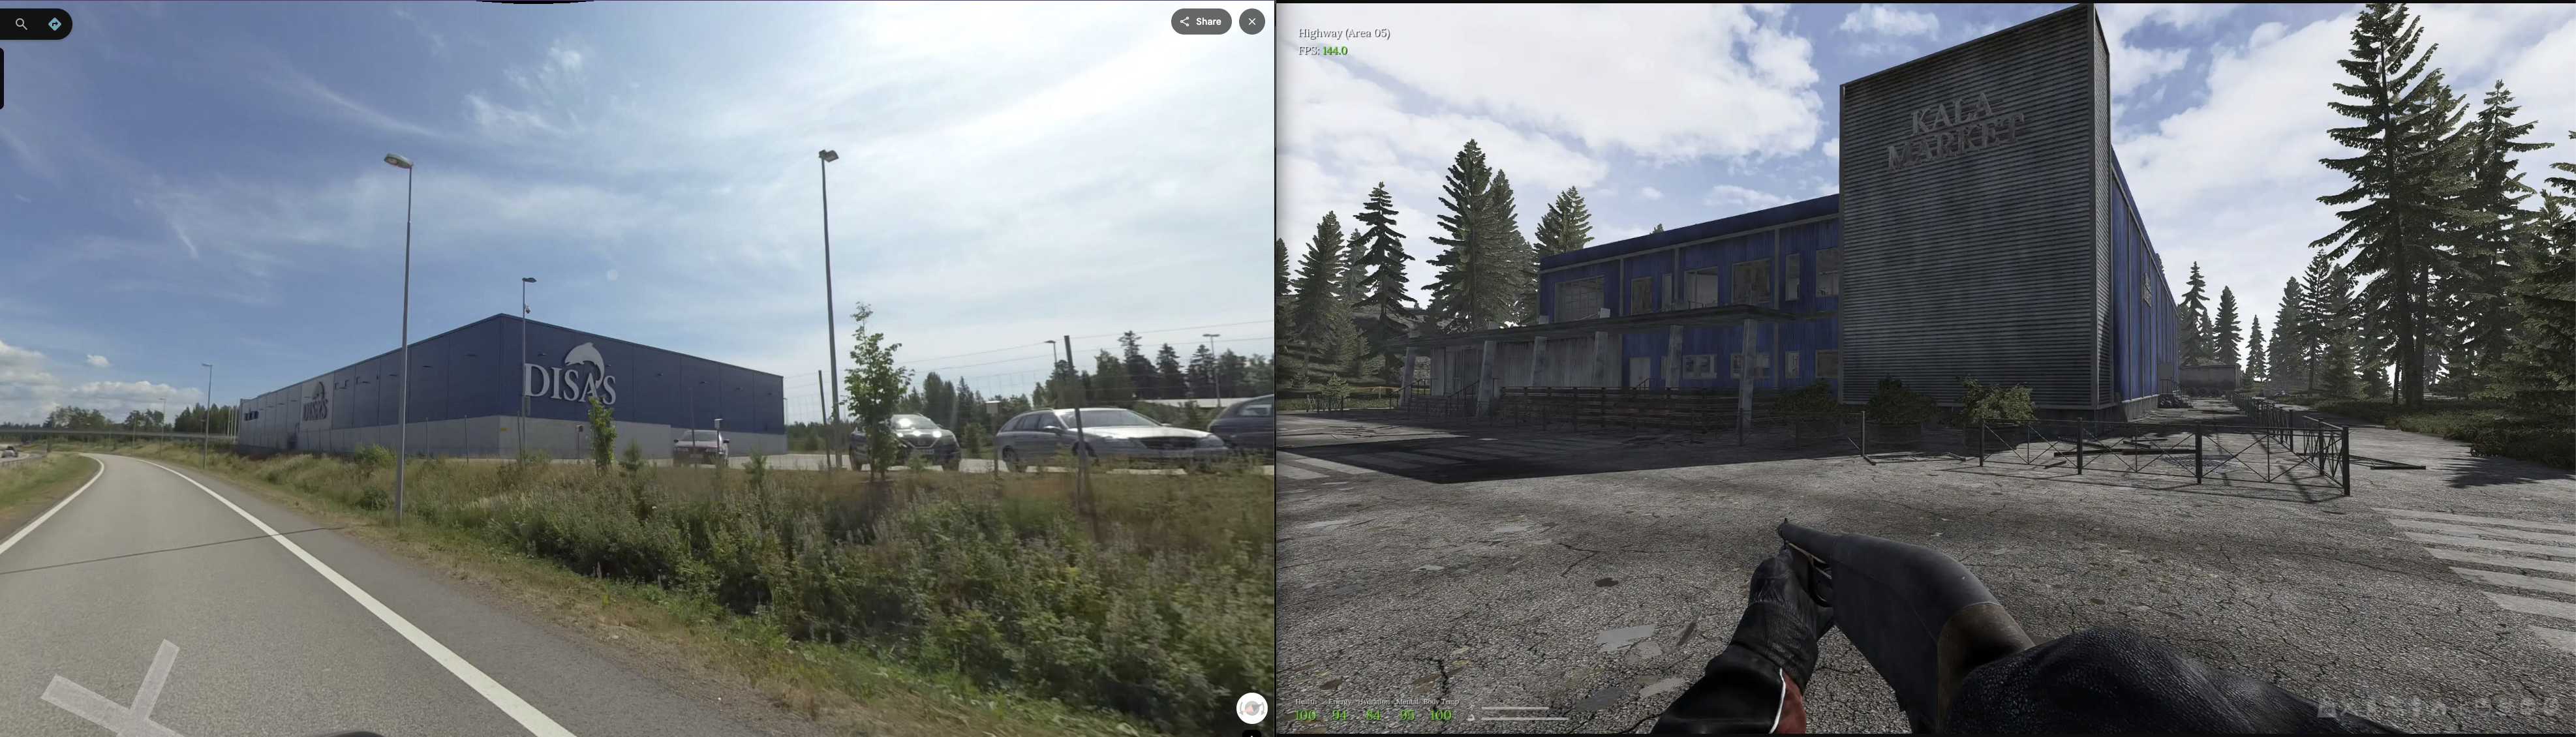
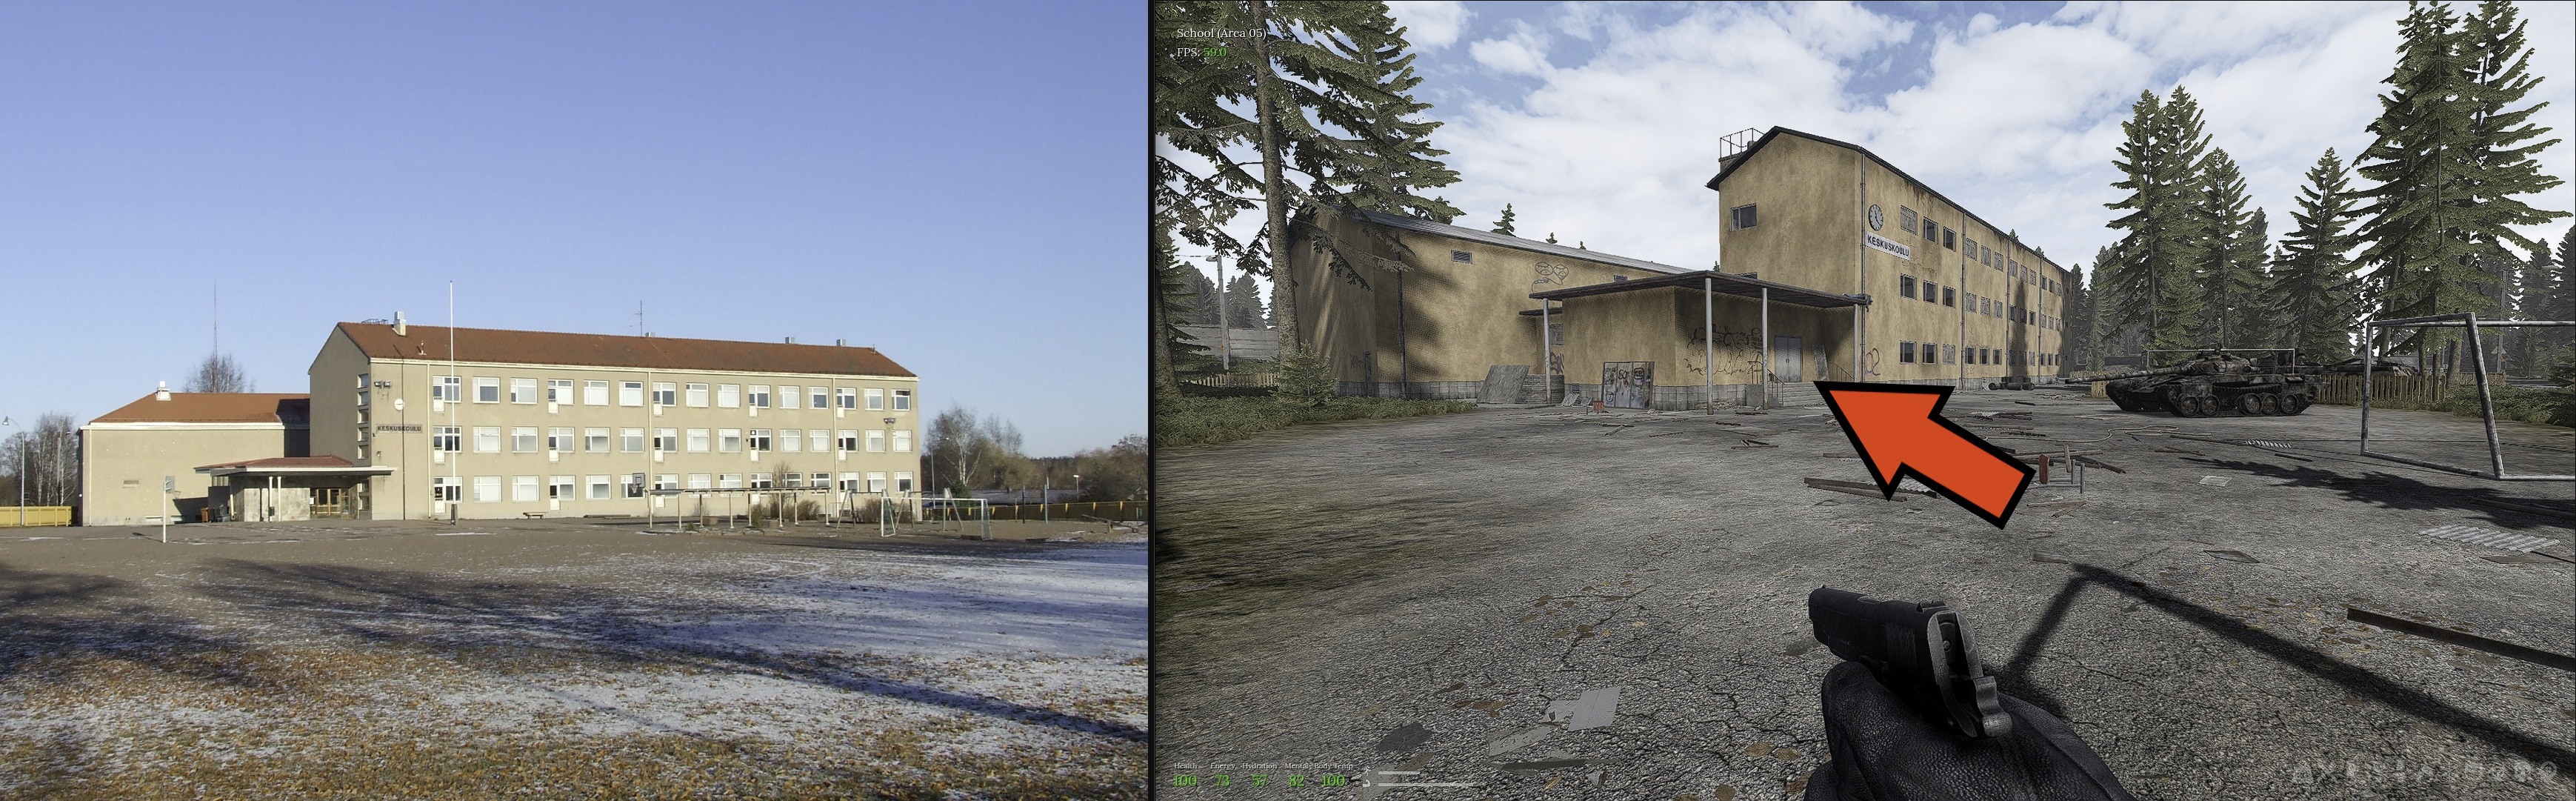
Road to Vostok is so accurate in locale and setting, it's uncanny. I grew up in a town next door, and did my military service in Hamina (many, many moons ago). https://store.steampowered.com/app/19636...
Harry Sintonen profile picture
How accurate is Road to Vostok vs real locations, you ask? Very. These are just a couple of examples.

The locations aren't 100% 1:1 though, to accommodate smoother gameplay, but you can see familiar places all the time.

#roadtovostok


Harry Sintonen · 21w
How accurate is Road to Vostok vs real locations, you ask? Very. These are just a couple of examples. The locations aren't 100% 1:1 though, to accommodate smoother gameplay, but you can see familiar places all the time. #roadtovostok https://media.infosec.exchange/infosec.exchange/media_attachmen...
Till Kleisli · 30w
nostr:nprofile1qy2hwumn8ghj7un9d3shjtnyd968gmewwp6kyqpqmvfdung5whdgpwwllyqjggm5lrh4wylvjw3kgex9dxzcsjuc75fsgnuygl Unless you have a server in your basement or you have encrypted all data, it doesn't protect your data from the authorities, because also hosting providers will hand over data "in compli...
Harry Sintonen profile picture
This should be obvious for everyone by now, but if you're not from US you must assume that all your use of US AI services (#ChatGPT, #Claude, #Gemini etc) is fed directly to US intelligence services.

"We may share your Personal Data, including information about your interaction with our Services, with government authorities ... in compliance with the law (i)" (OpenAI)

"We may disclose personal data to governmental regulatory authorities as required by law" (Claude)

"We will share personal information outside of Google ... to: Respond to any applicable law, regulation, legal process, or enforceable governmental request" (Gemini)

The amount of valuable information fed to the systems voluntarily is staggering. It's not a matter of "if" it is happening, but "of course it is". It would be outright negligent if they weren’t capturing and disseminating it all.

https://en.wikipedia.org/wiki/Foreign_Intelligence_Surveillance_Act#Without_a_court_order

#privacy
1
Till Kleisli · 30w
nostr:nprofile1qy2hwumn8ghj7un9d3shjtnyd968gmewwp6kyqpqmvfdung5whdgpwwllyqjggm5lrh4wylvjw3kgex9dxzcsjuc75fsgnuygl I assume every legally operated service is sharing data "in compliance with the law", also Mistral. The problem starts, when Donnie Trump is "the law" and/or when the company operates in...
Veit Schiele · 37w
There is a critical security vulnerability in zlib that allows code smuggling. Currently, there does not appear to be an update available. • https://seclists.org/fulldisclosure/2026/Jan/3 • https:...
Harry Sintonen profile picture
@nprofile1q... Considering this is in contrib/untgz application rather than the library itself is this really a major problem? Is any distro even including the contrib tools in any of their packages?

I'm somewhat doubt it considering contrib dir has this major warning:

"All files under this contrib directory are UNSUPPORTED. They were provided by users of zlib and were not tested by the authors of zlib. Use at your own risk. Please contact the authors of the contributions for help about these, not the zlib authors. Thanks."

https://github.com/madler/zlib/blob/develop/contrib/README.contrib
1
Veit Schiele · 37w
nostr:nprofile1qy2hwumn8ghj7un9d3shjtnyd968gmewwp6kyqpqmvfdung5whdgpwwllyqjggm5lrh4wylvjw3kgex9dxzcsjuc75fsgnuygl Even though the zlib authors do not consider themselves responsible, this is still classified as a critical security vulnerability.
tschenkel · 48w
nostr:nprofile1qyt8wumn8ghj7un9d3shjtnyd968gmewwp6kytcqyrd39hjdz36a4q9emluszfprwnuw74cnajf6xeryc45ctzztnr63xu4370p So this is how I learned that #signal is using #aws instead of their own hosting. Since #amazon has shown that they are willing to succumb to government pressure, I am wondering if ...
uvok Grumpyspots · 54w
nostr:nprofile1qy2hwumn8ghj7un9d3shjtnddaehgu3wwp6kyqpqmvfdung5whdgpwwllyqjggm5lrh4wylvjw3kgex9dxzcsjuc75fs7mqwua now I'm even more confused. Wasn't -L like always part of curl? But now I also see this in the man page The method set with -X, --request overrides the method curl would ...