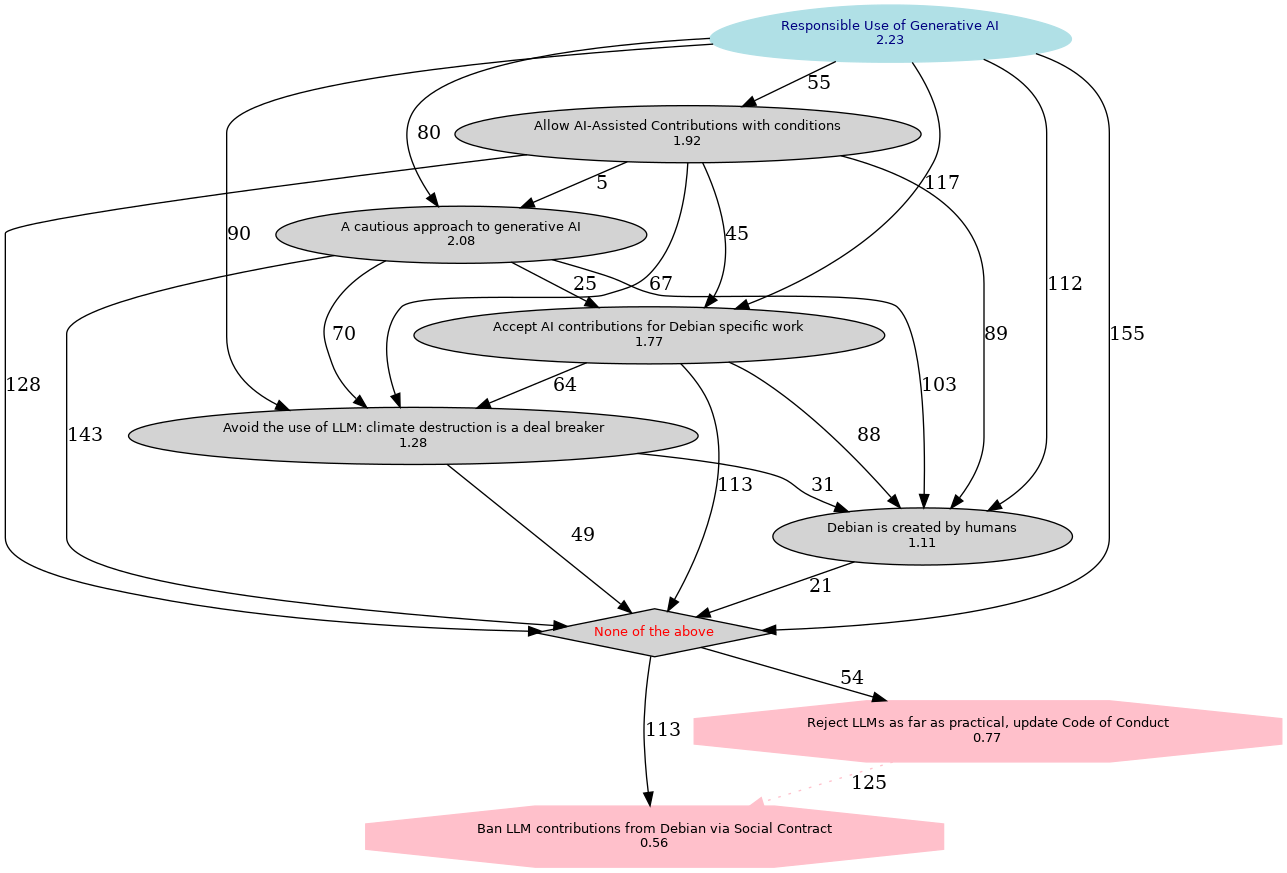
The directed graph of voting results for LLM usage is very Debian (and perhaps something applicable to mainstream voting on complex issues!) https://vote.debian.org/~secretary/gr_llm/
@nprofile1q... I think the software supply chain is so complex and intertwined now that they’d struggle to figure out who are what to fund! A success disaster of the commons
@nprofile1q... I agree with you that nothing has structurally changed, but the ability to chain multiple exploits within seconds seems like a new capability...
I've had to respond to multiple OSS security issues recently and the wild thing is that agents can now generate exploits just on the *rumour* of a bug. This throws security embargoes out the window, as the fix is less important than the knowledge of its existence. What on earth are open source maintainers supposed to do next? https://anil.recoil.org/notes/rumour-is-the-exploit
@nprofile1q...@nprofile1q...@nprofile1q... I think this 'ePDF' is a rendering of the PDF and not HTML; it doesn't reflow on resize for example. I wonder where the TAPS HTML5 output goes, I cant find any papers in the DL that expose it.
I'm delighted to announce that our formerly plain PDF ICFP 2026 paper (https://anil.recoil.org/papers/2026-package-calculus.pdf) has been UPGRADED with advanced AI summaries (if you pay up for the premium ACM account) and is under impenetrable cybersecurity protection (if you click through painful captchas and wait 10 seconds) and is way slower due to being hidden behind a web-based epdf reader rather than using your native PDF client. https://dl.acm.org/doi/10.1145/3828699.
Seeing so many LLM-based spam attacks hitting my elderly relatives now. And meanwhile, I have to explain why the 'Apple Store' is not the same as the 'App Store'. We've collectively made a hash of partitioning trust in mobile devices, while making them a centrepoint of identity online