

🚨🇧🇷 Medgrupo and FUSVE patient data allegedly leaked and offered on a cybercrime forum
⠀
Medgrupo is a Brazilian medical education company, while FUSVE operates educational and healthcare institutions in Rio de Janeiro state, including Vassouras University Hospital.
⠀
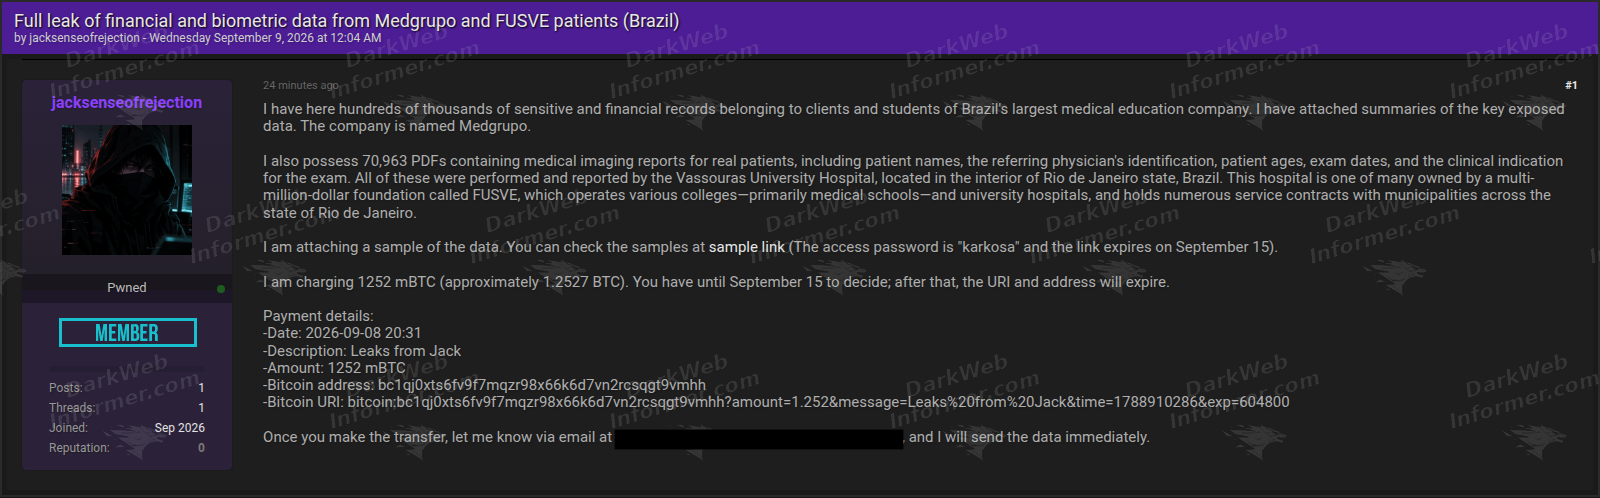
A threat actor using the handle jacksenseofrejection claims to possess hundreds of thousands of sensitive and financial records associated with Medgrupo clients and students, along with 70,963 PDF medical imaging reports involving patients of Vassouras University Hospital.
⠀
Claimed exposed data includes:
⠀
• Client and student financial records
• Patient names
• Patient ages
• Referring physician information
• Medical imaging reports
• Examination dates
• Clinical indications
• Other sensitive medical information
⠀
The actor published samples and is asking approximately 1.25 BTC for the purported data, with an offer deadline of September 15, 2026.
⠀
The breach claim, origin of the data, and full scope of the exposure have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
⠀
Medgrupo is a Brazilian medical education company, while FUSVE operates educational and healthcare institutions in Rio de Janeiro state, including Vassouras University Hospital.
⠀
A threat actor using the handle jacksenseofrejection claims to possess hundreds of thousands of sensitive and financial records associated with Medgrupo clients and students, along with 70,963 PDF medical imaging reports involving patients of Vassouras University Hospital.
⠀
Claimed exposed data includes:
⠀
• Client and student financial records
• Patient names
• Patient ages
• Referring physician information
• Medical imaging reports
• Examination dates
• Clinical indications
• Other sensitive medical information
⠀
The actor published samples and is asking approximately 1.25 BTC for the purported data, with an offer deadline of September 15, 2026.
⠀
The breach claim, origin of the data, and full scope of the exposure have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing